
Agentic SOC Platform
Quick Start ·
Learn More ·
Workspace Features


**Agentic SOC Platform** is an open-source security operations platform built on Agentic AI, enabling agents to proactively participate in triage, investigation, enrichment, and knowledge accumulation so security teams can move from alert fatigue to AI-assisted decision-making.
---
### Alert Floods, Converged into Actionable Cases
Modules stream SIEM / Webhook alerts, extract IOCs, correlate related signals, and generate Cases, Alerts, and Artifacts so massive log volumes converge into a small number of actionable cases.

### AI-Powered Investigation, Seconds Not Hours
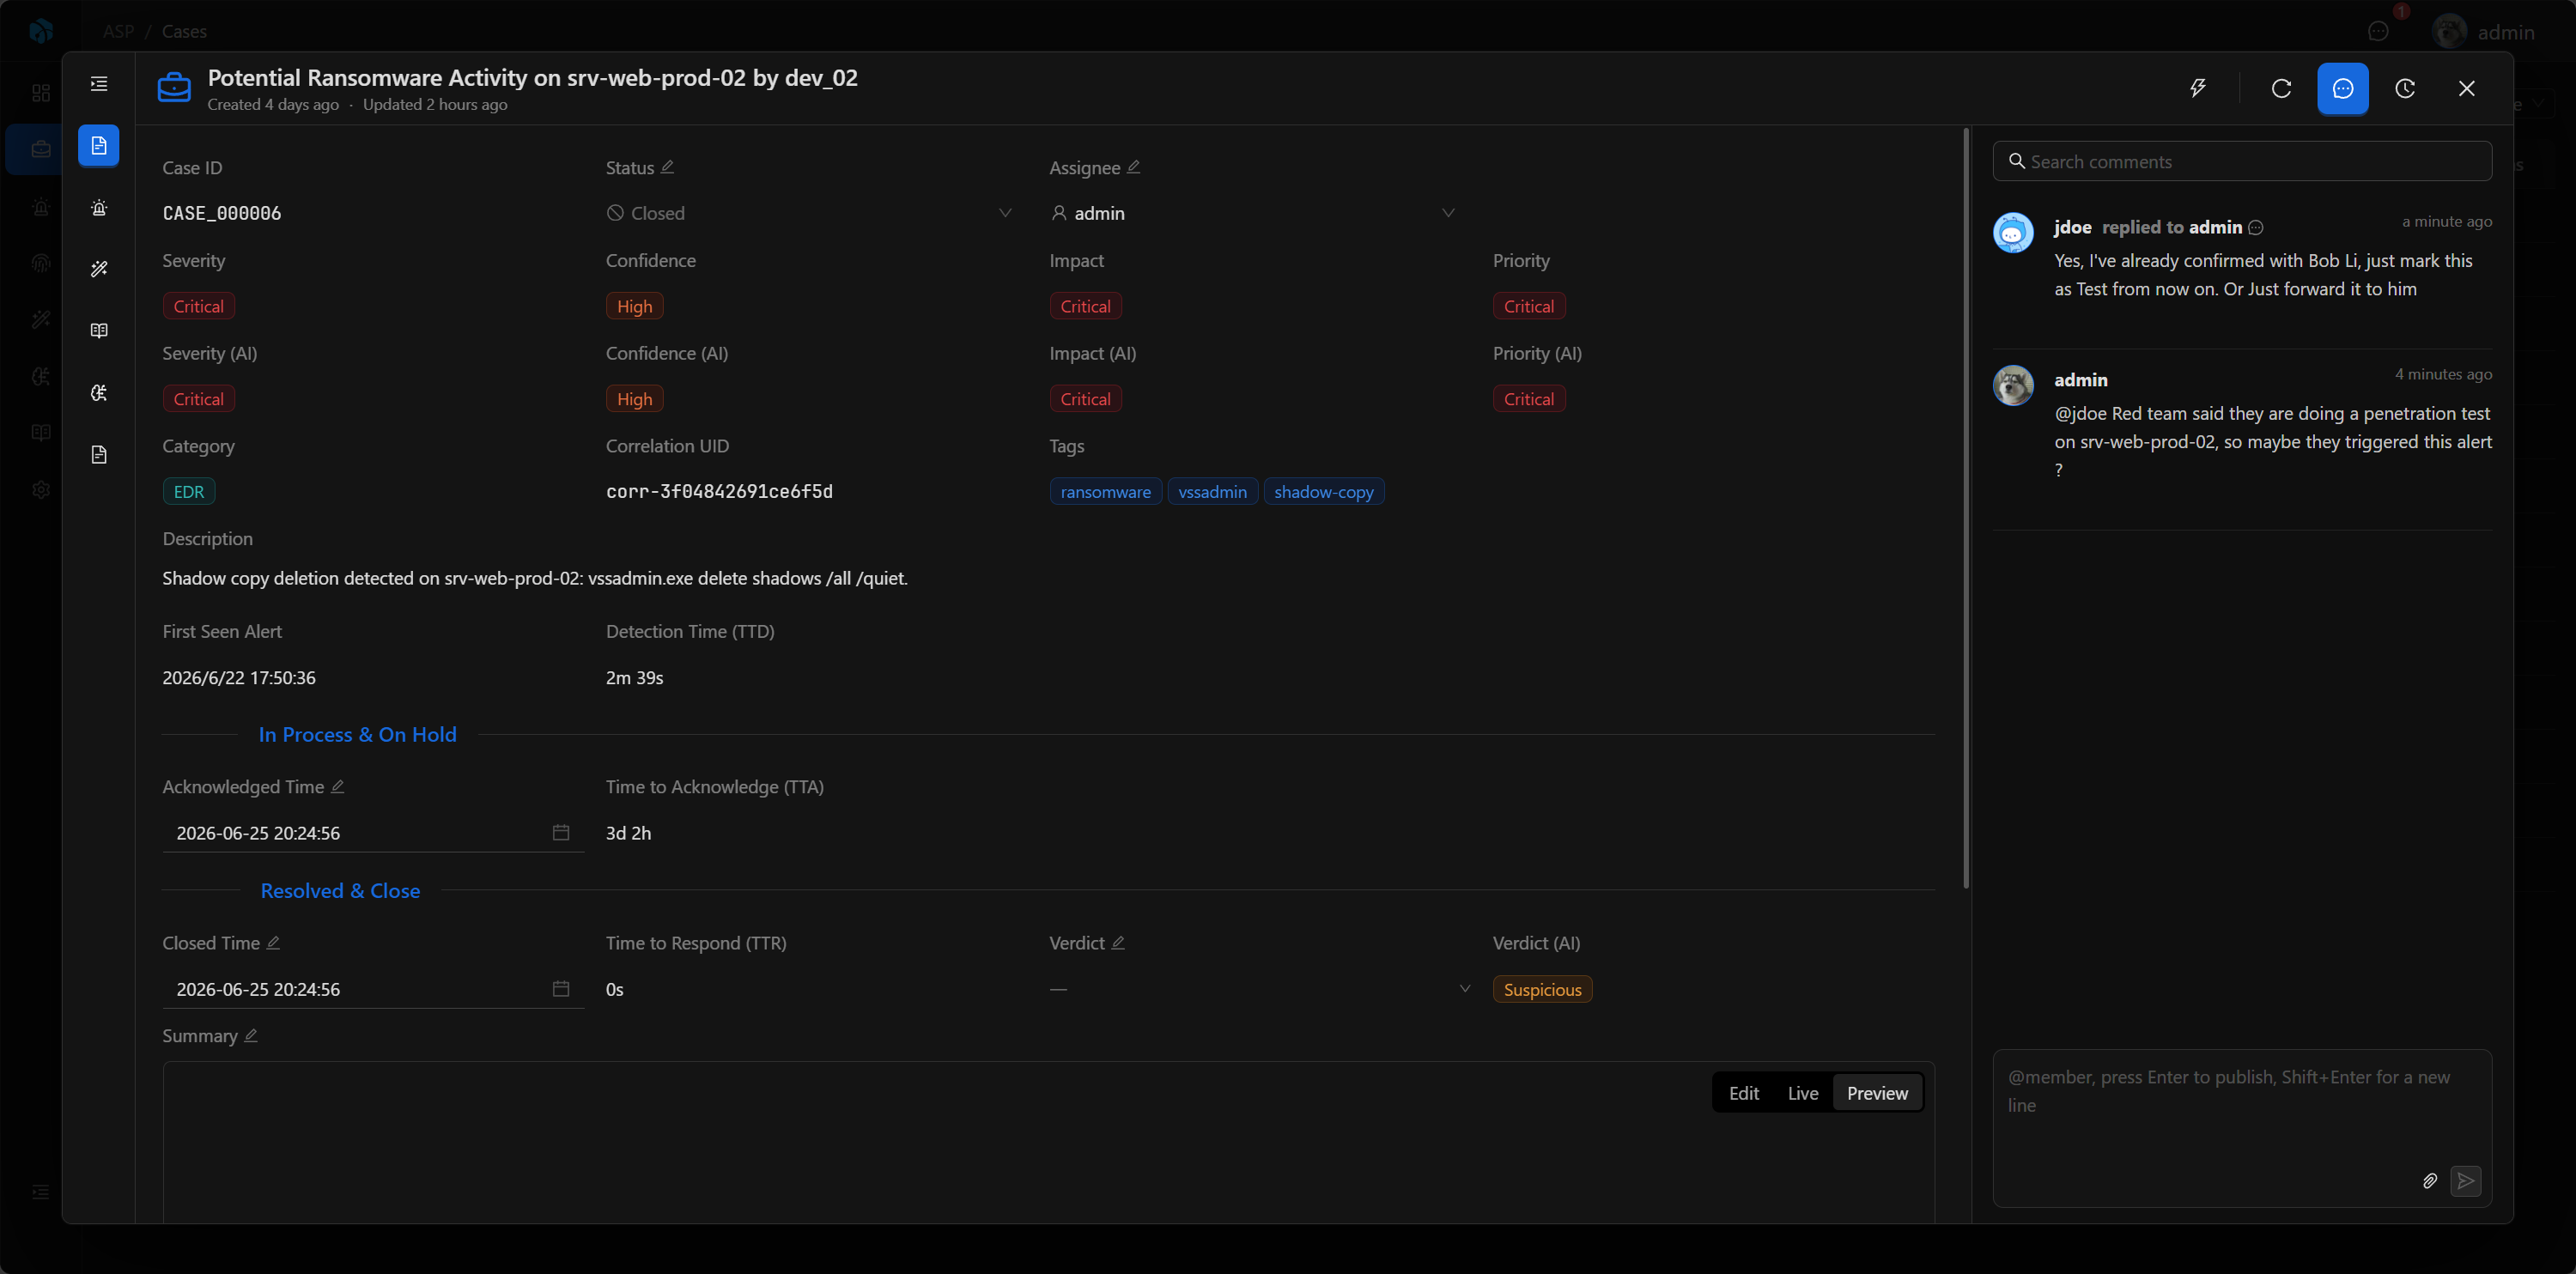
Compress hours of manual analysis into seconds, automatically producing severity, confidence, impact, priority, verdicts, and structured investigation reports.

### One Click to Drive Complex Investigations
Launch LLM investigation, knowledge extraction, threat intelligence enrichment, and CMDB enrichment around each Case, orchestrating traditional SOAR workflows and AI analysis in the same Playbook system.

### Deep Harness Agent Integration
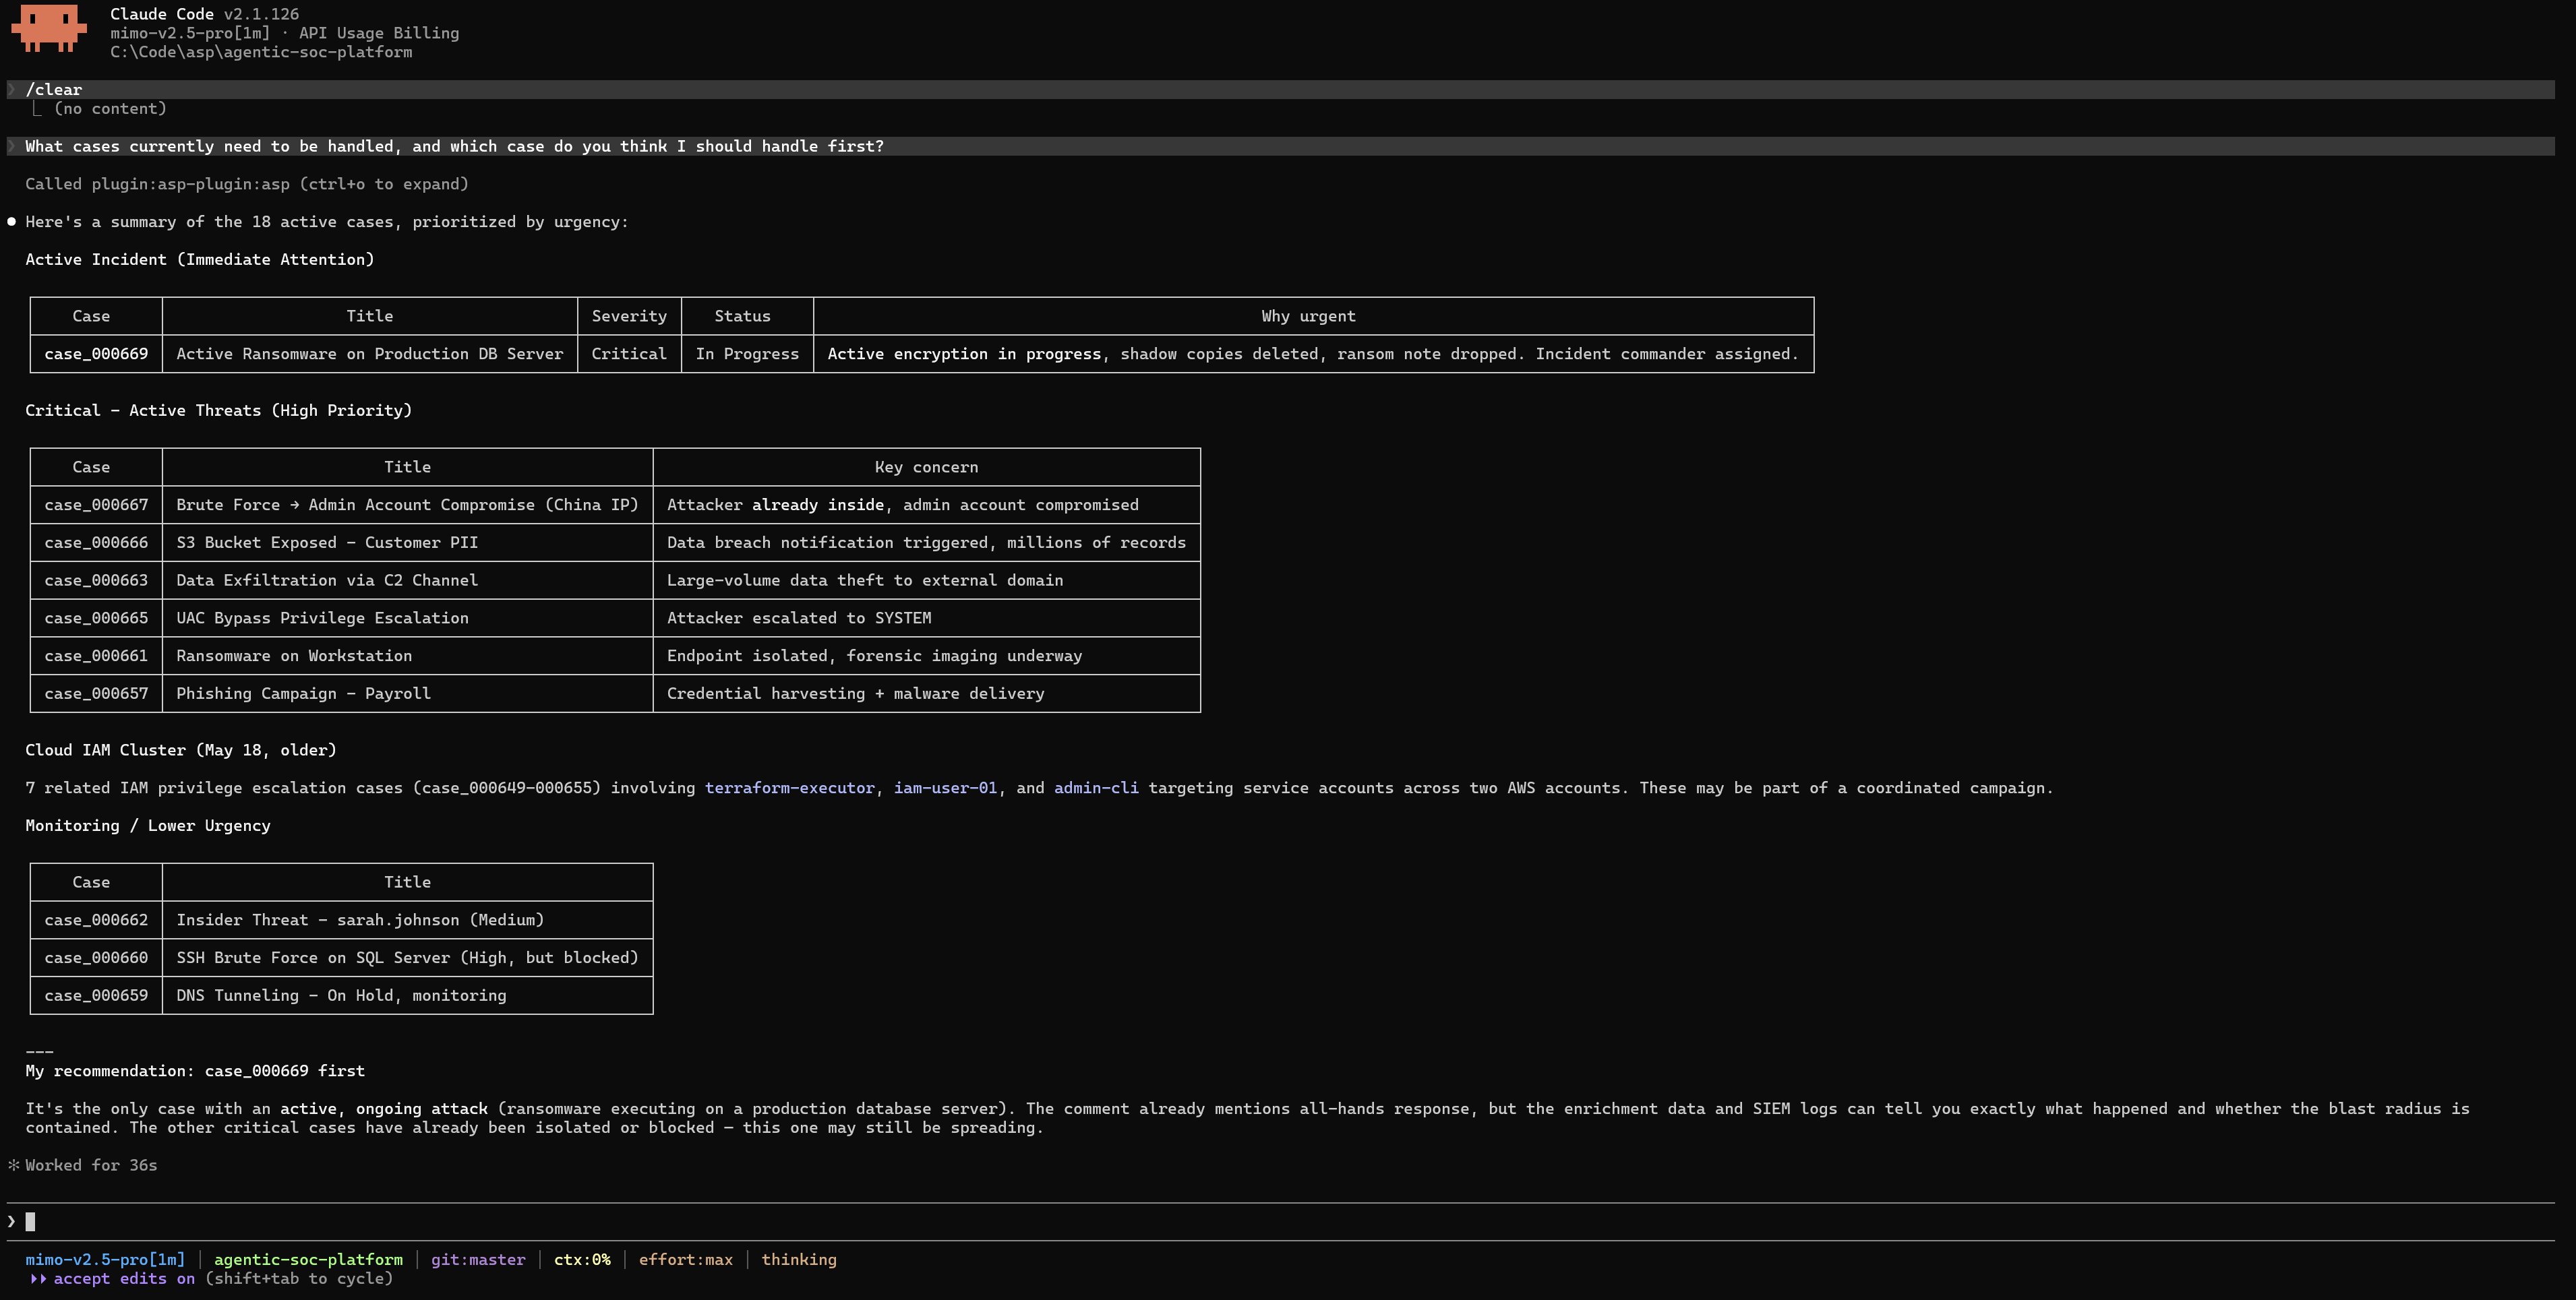
Expose ASP capabilities to Claude Code / Codex / OpenCode and other Harness Agents through the CLI and plugins, enabling agents to operate Cases, search logs, query threat intelligence, and write modules and playbooks directly.
### Multi-SIEM Access, One Investigation Entry Point
Support Splunk, ELK configuration, unified log search, and Webhook alert ingestion so LLMs, agents, and analysts all work with the same security context.

### Automated Threat Intelligence Enrichment
Automatically enrich IOCs and Artifacts with reputation, pulses, asset, identity, and historical context so every suspicious entity appears with evidence for judgment.

### Knowledge Accumulation, Smarter Over Time
Extract reusable knowledge from closed Case investigation records, response processes, and discussions, allowing organizational experience to grow with every response.

### Collaboration, Audit, and Access Control Built In
Local / LDAP login, user roles, API Keys, Inbox notifications, and Audit Log provide foundational governance so security operations no longer depend on fragmented tools.
### Low-Cost Adaptation, Highly Flexible Customization
Use Python Modules to adapt new SIEM rules and alert sources, and use Playbooks to orchestrate LLM analysis and automated actions so the platform grows with your security scenarios.

### Open Source, Private Deployment, Python & Typescript
MIT licensed, fully local deployment supported. Security data stays inside your network, while the backend, frontend, and extension scripts remain clear and controllable.
---
## Official Website
[https://asp.viperrtp.com](https://asp.viperrtp.com)
## 404Starlink
 Agentic SOC Platform has joined [404Starlink](https://github.com/knownsec/404StarLink)