mirror of
https://github.com/block/buzz.git
synced 2026-08-18 06:50:31 +02:00
 Taylor HoandGitHub
d8281b9c93
**Category:** new-feature **User Impact:** Mobile users must confirm with Face ID, biometrics, or their device passcode before sending their Buzz identity to Desktop. **Problem:** A signed-in phone could send its full identity, including the `nsec`, to a desktop without fresh local verification. **Solution:** Require OS device authentication before opening the identity-recovery scanner, retain that authorization only for the active pairing session and short pairing window, and require fresh authentication again if it expires before the identity payload is sent. Normal app opening, identity import, and community removal remain unchanged. ## Screencasts | Enable Face ID | Use Face ID | | --- | --- | | 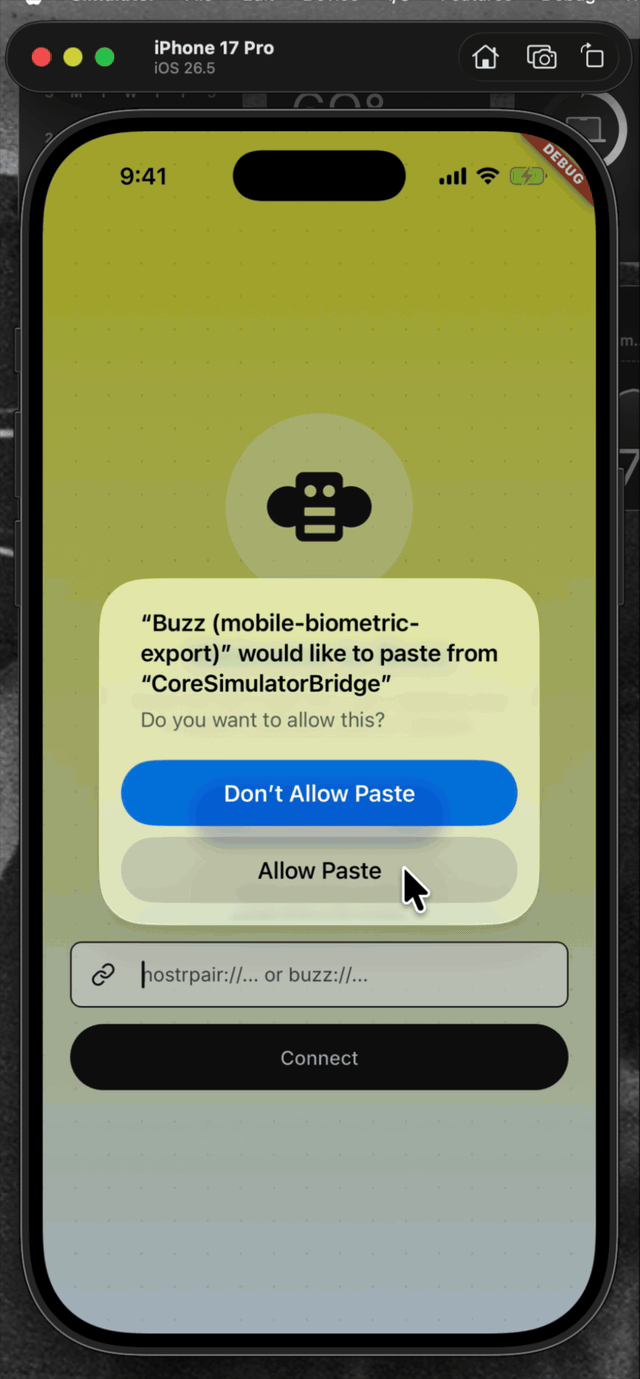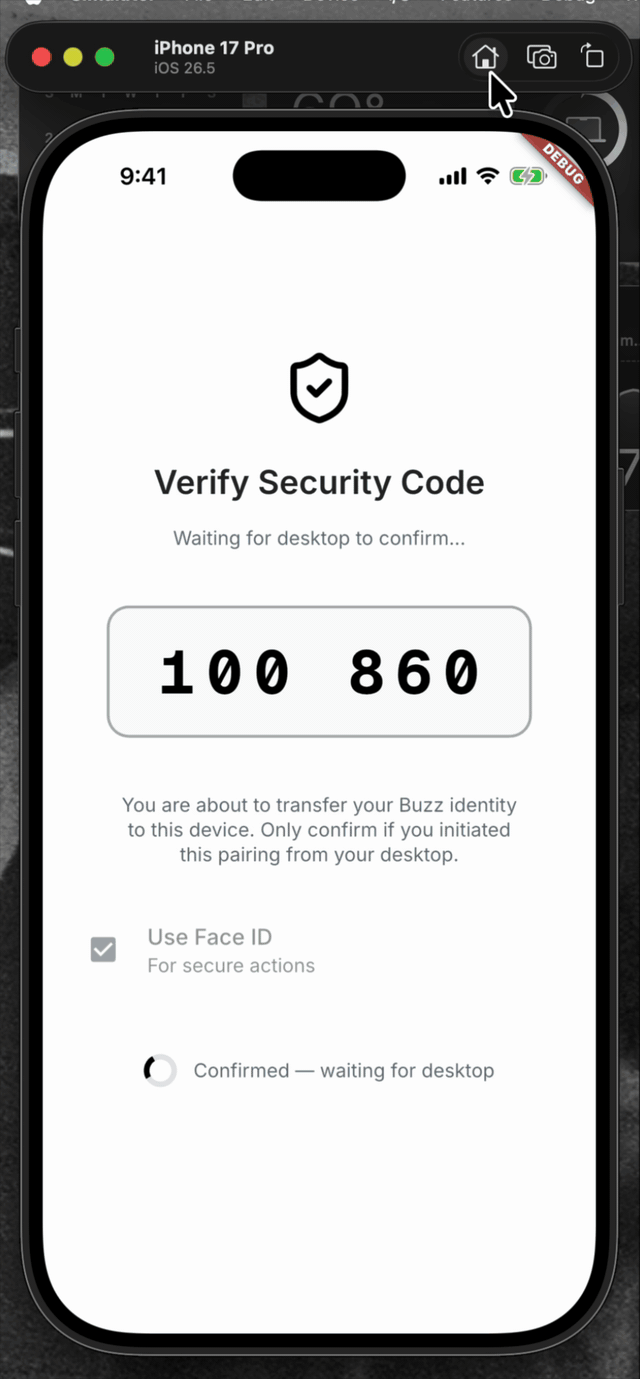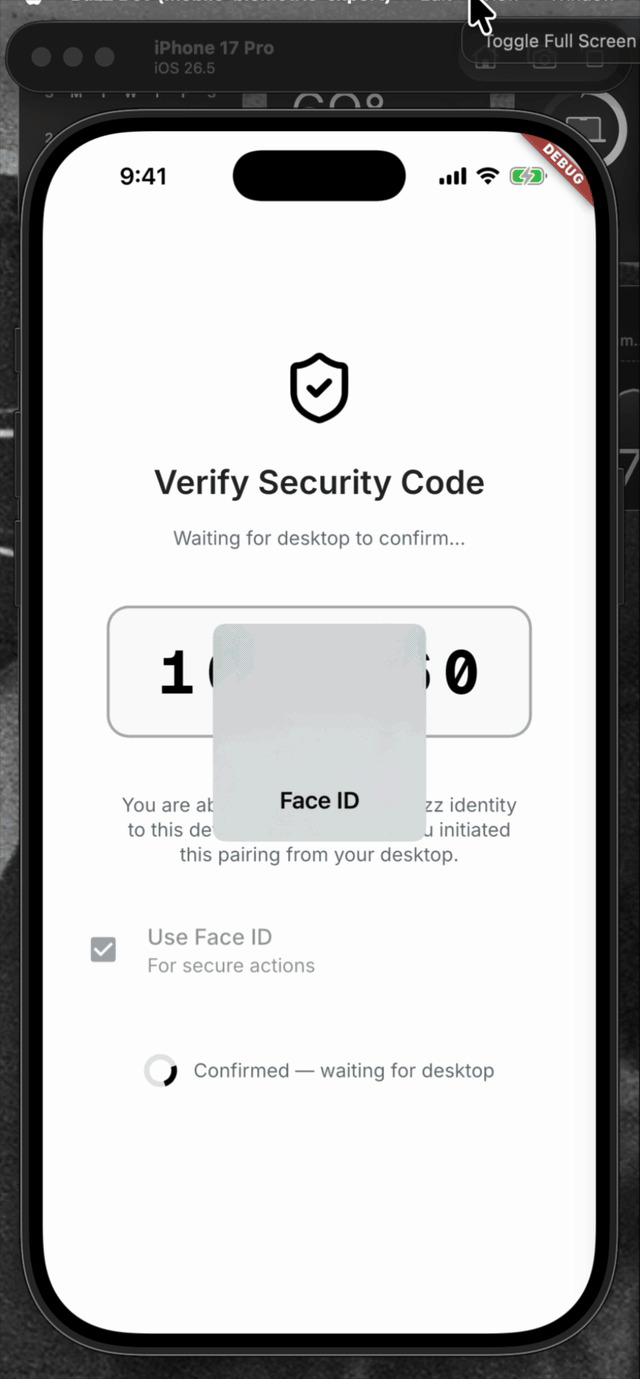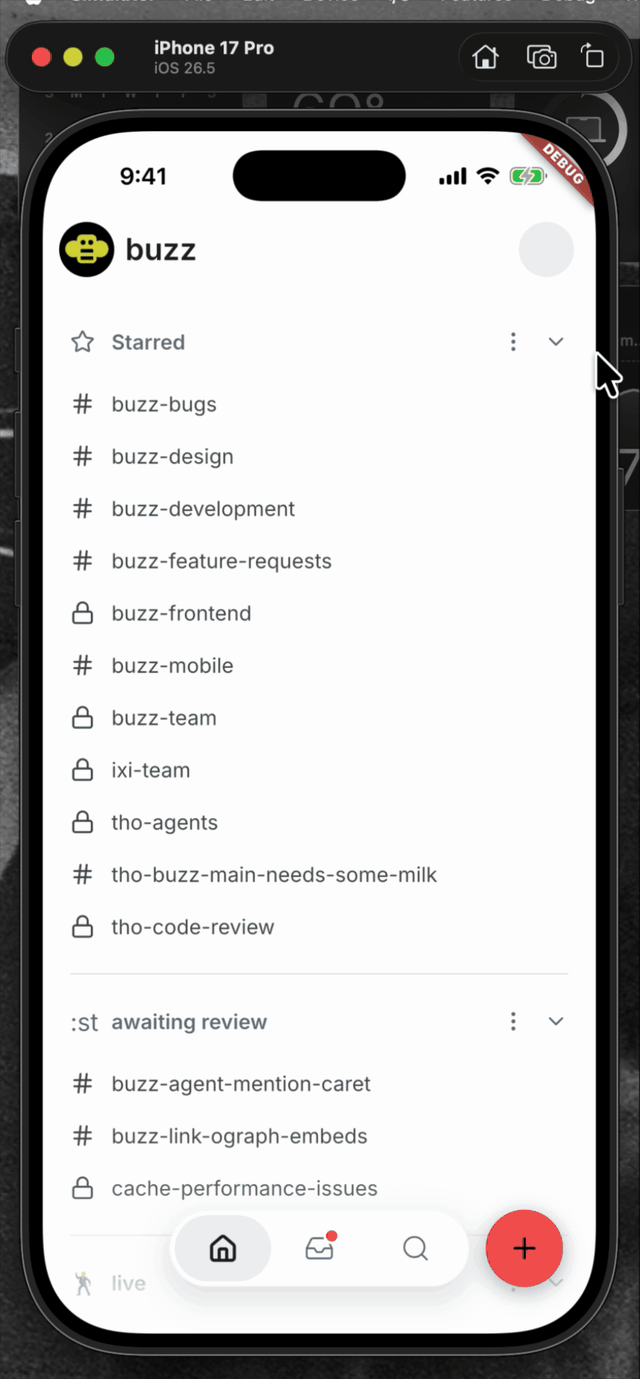 | 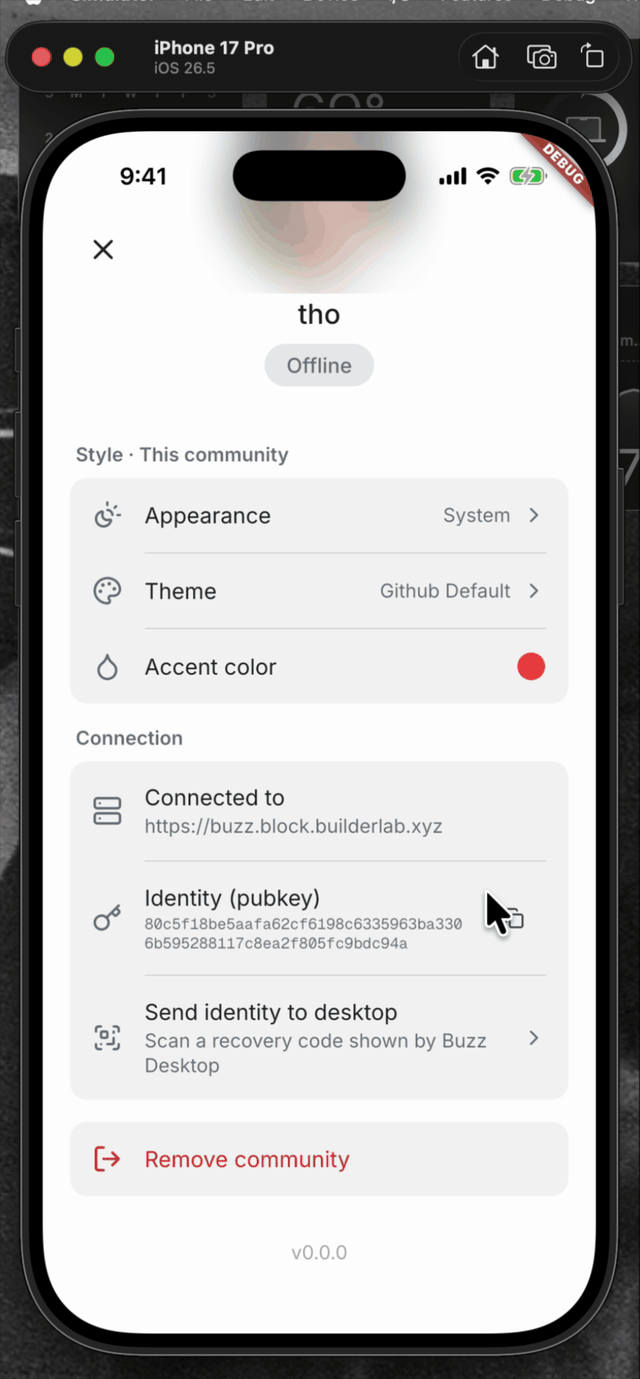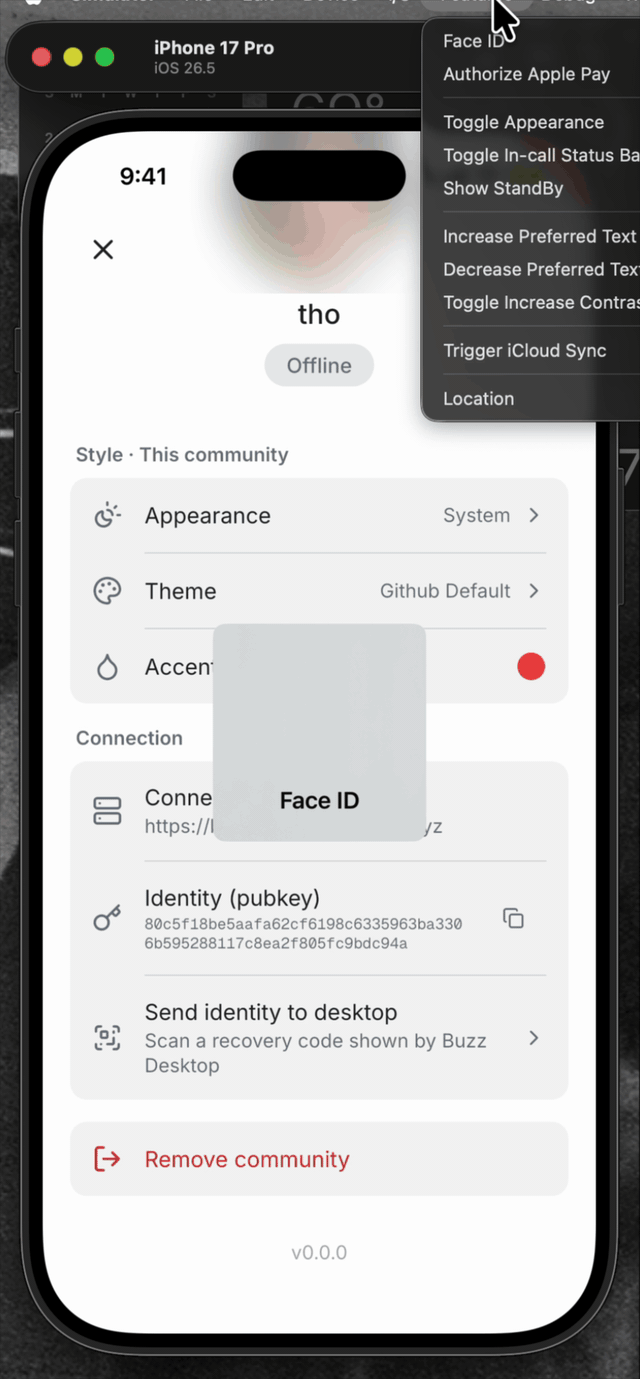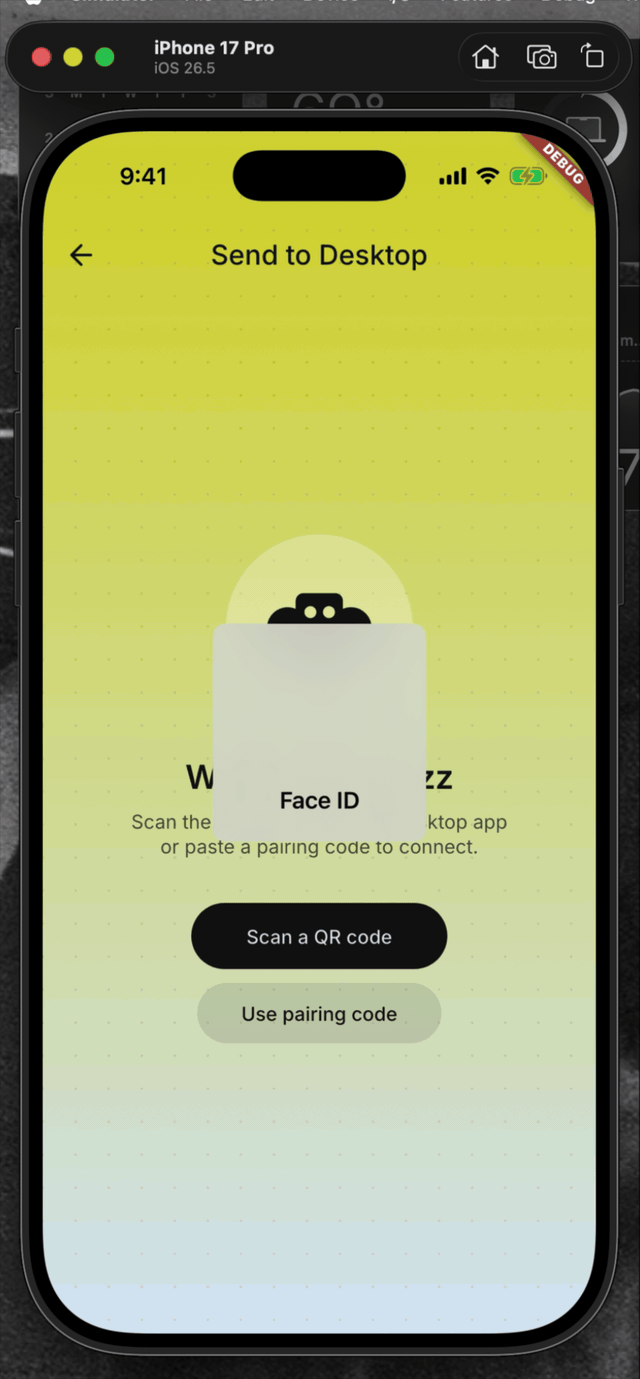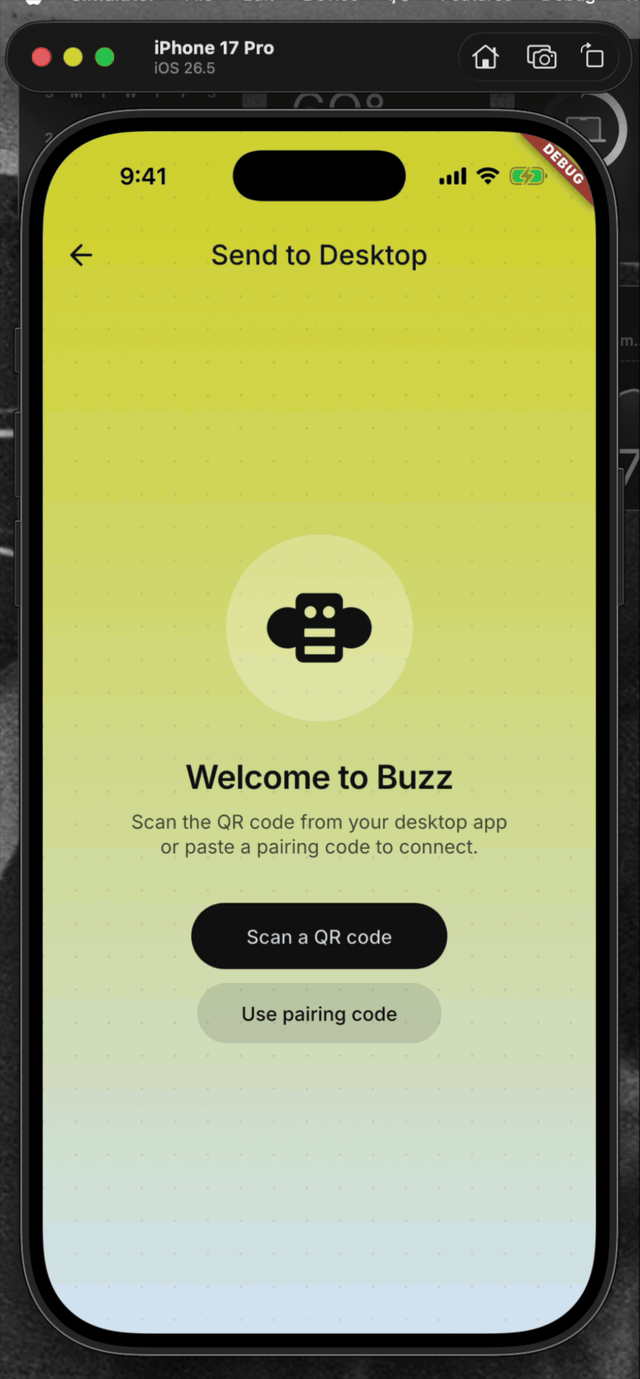 | <details> <summary>File changes</summary> **Android and iOS integration** - `mobile/android/app/build.gradle.kts` declares the AppCompat dependency required by the biometric activity theme. - `mobile/android/app/src/main/kotlin/xyz/block/buzz/mobile/MainActivity.kt` uses the activity type required by the system authentication prompt. - `mobile/android/app/src/main/res/values/styles.xml` and `mobile/android/app/src/main/res/values-night/styles.xml` use the compatible launch theme. - `mobile/ios/Podfile.lock` records the native local-authentication dependency. - `mobile/ios/Runner/Info.plist` explains why Buzz requests Face ID access. **Identity policy and pairing flow** - `mobile/lib/shared/security/sensitive_action_authorizer.dart` wraps OS authentication and maps platform errors to stable app-level outcomes. - `mobile/lib/shared/community/community.dart` and `mobile/lib/shared/community/community_storage.dart` persist the sensitive-action policy. - `mobile/lib/features/invites/invite_join_provider.dart` assigns the explicit policy for invite-created communities. - `mobile/lib/features/pairing/pairing_provider.dart` gates export, binds grants to the active community/session, reauthenticates expired grants, and clears grants on every terminal path. - `mobile/lib/features/pairing/pairing_page.dart` lets users choose biometric protection while importing an identity. - `mobile/lib/features/settings/settings_page.dart` wires pairing into settings. - `mobile/lib/features/settings/settings_page/connection_section.dart` authenticates before opening export recovery and bounds the foreground-resume wait. - `mobile/pubspec.yaml` and `mobile/pubspec.lock` add and lock `local_auth`. **Coverage** - `mobile/test/shared/security/sensitive_action_authorizer_test.dart` covers native result mapping, unsupported devices, and single-flight behavior. - `mobile/test/shared/community/community_test.dart` and `mobile/test/shared/community/community_storage_test.dart` cover policy defaults and persistence. - `mobile/test/features/invites/invite_join_provider_test.dart` covers the invite policy. - `mobile/test/features/pairing/pairing_page_test.dart` covers import protection controls. - `mobile/test/features/pairing/pairing_provider_test.dart` covers export/import authorization, stale/reset/concurrent guards, malformed payload cleanup, and no-export failure paths. - `mobile/test/features/settings/connection_section_test.dart` covers the tap gate, lifecycle resume, and timeout behavior. </details> ## Reproduction steps 1. Pair an identity into the mobile app. 2. Open Settings and choose “Send identity to desktop.” 3. Verify Face ID, biometrics, or the device passcode is required before the recovery scanner opens. 4. Cancel device authentication and verify the scanner does not open and no identity transfer begins. 5. Authenticate, scan a Desktop recovery code, confirm the SAS, and verify the identity transfer completes. ## Validation At `be5620f5f10aa6cc16e86a4f01f102f3d9aeef9b`: - `cd mobile && ../bin/flutter analyze` — no issues - `cd mobile && ../bin/flutter test` — 1,368 tests passed - `cd mobile/android && JAVA_HOME=$(/usr/libexec/java_home -v 21) ./gradlew app:assembleDebug` — debug APK assembled successfully --------- Signed-off-by: Taylor Ho <taylorkmho@gmail.com>


259 lines
8.3 KiB
Dart
259 lines
8.3 KiB
Dart
import 'dart:async';
|
|
|
|
import 'package:buzz/features/pairing/pairing_provider.dart';
|
|
import 'package:buzz/features/settings/settings_page.dart';
|
|
import 'package:buzz/shared/auth/auth.dart';
|
|
import 'package:buzz/shared/relay/relay.dart';
|
|
import 'package:buzz/shared/theme/theme.dart';
|
|
import 'package:flutter/material.dart';
|
|
import 'package:flutter_test/flutter_test.dart';
|
|
import 'package:nostr/nostr.dart' as nostr;
|
|
import 'package:shared_preferences/shared_preferences.dart';
|
|
|
|
import '../../helpers/widget_helpers.dart';
|
|
|
|
void main() {
|
|
testWidgets('waits for a resumed frame before navigating after auth', (
|
|
tester,
|
|
) async {
|
|
final authorization = Completer<bool>();
|
|
final pairing = _PairingNotifier(authorization.future);
|
|
SharedPreferences.setMockInitialValues({});
|
|
final prefs = await SharedPreferences.getInstance();
|
|
|
|
await tester.pumpWidget(
|
|
WidgetHelpers.testable(
|
|
overrides: [
|
|
relayConfigProvider.overrideWith(_RelayConfigNotifier.new),
|
|
authProvider.overrideWith(_AuthNotifier.new),
|
|
pairingProvider.overrideWith(() => pairing),
|
|
savedPrefsProvider.overrideWithValue(prefs),
|
|
],
|
|
child: SettingsPage(
|
|
profileHeader: const SizedBox.shrink(),
|
|
invitePageBuilder: (_) => const SizedBox.shrink(),
|
|
identityRecoveryPageBuilder: (_) =>
|
|
const Scaffold(body: Text('Identity recovery')),
|
|
),
|
|
),
|
|
);
|
|
await tester.pump();
|
|
|
|
await tester.tap(find.text('Send identity to desktop'));
|
|
await tester.pump();
|
|
tester.binding.handleAppLifecycleStateChanged(AppLifecycleState.inactive);
|
|
authorization.complete(true);
|
|
await tester.pump();
|
|
|
|
expect(find.text('Identity recovery'), findsNothing);
|
|
|
|
tester.binding.handleAppLifecycleStateChanged(AppLifecycleState.resumed);
|
|
await tester.pump();
|
|
await tester.pump();
|
|
await tester.pumpAndSettle();
|
|
|
|
expect(find.text('Identity recovery'), findsOneWidget);
|
|
});
|
|
testWidgets('resume timeout keeps identity recovery closed', (tester) async {
|
|
final pairing = _PairingNotifier(Future<bool>.value(true));
|
|
SharedPreferences.setMockInitialValues({});
|
|
final prefs = await SharedPreferences.getInstance();
|
|
|
|
await tester.pumpWidget(
|
|
WidgetHelpers.testable(
|
|
overrides: [
|
|
relayConfigProvider.overrideWith(_RelayConfigNotifier.new),
|
|
authProvider.overrideWith(_AuthNotifier.new),
|
|
pairingProvider.overrideWith(() => pairing),
|
|
savedPrefsProvider.overrideWithValue(prefs),
|
|
],
|
|
child: SettingsPage(
|
|
profileHeader: const SizedBox.shrink(),
|
|
invitePageBuilder: (_) => const SizedBox.shrink(),
|
|
identityRecoveryPageBuilder: (_) =>
|
|
const Scaffold(body: Text('Identity recovery')),
|
|
),
|
|
),
|
|
);
|
|
await tester.pump();
|
|
tester.binding.handleAppLifecycleStateChanged(AppLifecycleState.inactive);
|
|
|
|
await tester.tap(find.text('Send identity to desktop'));
|
|
await tester.pump();
|
|
await tester.pump(const Duration(seconds: 5));
|
|
await tester.pump();
|
|
|
|
expect(pairing.resetCalls, 1);
|
|
expect(find.text('Identity recovery'), findsNothing);
|
|
expect(
|
|
find.text('Buzz did not return to the foreground. Try again.'),
|
|
findsOneWidget,
|
|
);
|
|
});
|
|
|
|
testWidgets('clears authorization when disposed during authentication', (
|
|
tester,
|
|
) async {
|
|
final authorization = Completer<bool>();
|
|
final pairing = _PairingNotifier(authorization.future);
|
|
SharedPreferences.setMockInitialValues({});
|
|
final prefs = await SharedPreferences.getInstance();
|
|
|
|
await tester.pumpWidget(
|
|
WidgetHelpers.testable(
|
|
overrides: [
|
|
relayConfigProvider.overrideWith(_RelayConfigNotifier.new),
|
|
authProvider.overrideWith(_AuthNotifier.new),
|
|
pairingProvider.overrideWith(() => pairing),
|
|
savedPrefsProvider.overrideWithValue(prefs),
|
|
],
|
|
child: SettingsPage(
|
|
profileHeader: const SizedBox.shrink(),
|
|
invitePageBuilder: (_) => const SizedBox.shrink(),
|
|
identityRecoveryPageBuilder: (_) =>
|
|
const Scaffold(body: Text('Identity recovery')),
|
|
),
|
|
),
|
|
);
|
|
await tester.pump();
|
|
|
|
final settingsContext = tester.element(
|
|
find.text('Send identity to desktop'),
|
|
);
|
|
await tester.tap(find.text('Send identity to desktop'));
|
|
await tester.pump();
|
|
unawaited(
|
|
Navigator.of(settingsContext).pushReplacement(
|
|
MaterialPageRoute<void>(builder: (_) => const SizedBox.shrink()),
|
|
),
|
|
);
|
|
await tester.pumpAndSettle();
|
|
authorization.complete(true);
|
|
await tester.pump();
|
|
|
|
expect(pairing.resetCalls, 1);
|
|
expect(find.text('Identity recovery'), findsNothing);
|
|
});
|
|
|
|
testWidgets('clears authorization when disposed during resume wait', (
|
|
tester,
|
|
) async {
|
|
final pairing = _PairingNotifier(Future<bool>.value(true));
|
|
SharedPreferences.setMockInitialValues({});
|
|
final prefs = await SharedPreferences.getInstance();
|
|
|
|
await tester.pumpWidget(
|
|
WidgetHelpers.testable(
|
|
overrides: [
|
|
relayConfigProvider.overrideWith(_RelayConfigNotifier.new),
|
|
authProvider.overrideWith(_AuthNotifier.new),
|
|
pairingProvider.overrideWith(() => pairing),
|
|
savedPrefsProvider.overrideWithValue(prefs),
|
|
],
|
|
child: SettingsPage(
|
|
profileHeader: const SizedBox.shrink(),
|
|
invitePageBuilder: (_) => const SizedBox.shrink(),
|
|
identityRecoveryPageBuilder: (_) =>
|
|
const Scaffold(body: Text('Identity recovery')),
|
|
),
|
|
),
|
|
);
|
|
await tester.pump();
|
|
tester.binding.handleAppLifecycleStateChanged(AppLifecycleState.inactive);
|
|
|
|
final settingsContext = tester.element(
|
|
find.text('Send identity to desktop'),
|
|
);
|
|
await tester.tap(find.text('Send identity to desktop'));
|
|
await tester.pump();
|
|
unawaited(
|
|
Navigator.of(settingsContext).pushReplacement(
|
|
MaterialPageRoute<void>(builder: (_) => const SizedBox.shrink()),
|
|
),
|
|
);
|
|
await tester.pumpAndSettle();
|
|
await tester.pump(const Duration(seconds: 5));
|
|
await tester.pump();
|
|
|
|
expect(pairing.resetCalls, 1);
|
|
expect(find.text('Identity recovery'), findsNothing);
|
|
});
|
|
|
|
testWidgets('denied authentication does not open identity recovery', (
|
|
tester,
|
|
) async {
|
|
final pairing = _PairingNotifier(Future<bool>.value(false));
|
|
SharedPreferences.setMockInitialValues({});
|
|
final prefs = await SharedPreferences.getInstance();
|
|
|
|
await tester.pumpWidget(
|
|
WidgetHelpers.testable(
|
|
overrides: [
|
|
relayConfigProvider.overrideWith(_RelayConfigNotifier.new),
|
|
authProvider.overrideWith(_AuthNotifier.new),
|
|
pairingProvider.overrideWith(() => pairing),
|
|
savedPrefsProvider.overrideWithValue(prefs),
|
|
],
|
|
child: SettingsPage(
|
|
profileHeader: const SizedBox.shrink(),
|
|
invitePageBuilder: (_) => const SizedBox.shrink(),
|
|
identityRecoveryPageBuilder: (_) =>
|
|
const Scaffold(body: Text('Identity recovery')),
|
|
),
|
|
),
|
|
);
|
|
await tester.pump();
|
|
|
|
await tester.tap(find.text('Send identity to desktop'));
|
|
await tester.pumpAndSettle();
|
|
|
|
expect(pairing.authorizationCalls, 1);
|
|
expect(find.text('Identity recovery'), findsNothing);
|
|
});
|
|
}
|
|
|
|
class _AuthNotifier extends AuthNotifier {
|
|
@override
|
|
Future<AuthState> build() async => AuthState(
|
|
status: AuthStatus.authenticated,
|
|
community: Community(
|
|
id: 'community',
|
|
name: 'Test',
|
|
relayUrl: 'https://relay.test',
|
|
nsec: _RelayConfigNotifier.nsec,
|
|
addedAt: DateTime.utc(2026),
|
|
),
|
|
);
|
|
}
|
|
|
|
class _RelayConfigNotifier extends RelayConfigNotifier {
|
|
static final nsec = nostr.Keys(
|
|
'1111111111111111111111111111111111111111111111111111111111111111',
|
|
).nsec;
|
|
|
|
@override
|
|
RelayConfig build() => RelayConfig(baseUrl: 'https://relay.test', nsec: nsec);
|
|
}
|
|
|
|
class _PairingNotifier extends PairingNotifier {
|
|
_PairingNotifier(this.authorization);
|
|
|
|
final Future<bool> authorization;
|
|
int authorizationCalls = 0;
|
|
int resetCalls = 0;
|
|
|
|
@override
|
|
PairingState build() => const PairingState();
|
|
|
|
@override
|
|
Future<bool> authorizeIdentityExport({required Community community}) {
|
|
authorizationCalls++;
|
|
return authorization;
|
|
}
|
|
|
|
@override
|
|
void reset() {
|
|
resetCalls++;
|
|
}
|
|
}
|