Taylor Ho
8487e9fa5d
Merge origin/main into tho/nip49-ux-review
...
Conflict resolutions:
- desktop/src-tauri/src/relay.rs: take main's refactor that removes
submit_signed_event in favor of the exported
submit_signed_event_at_with_keys (relay/submit.rs); the auto-merge of
submit.rs already carried this branch's NIP-49 egress guard into that
function, so the guard coverage is preserved at the new choke point
- desktop/src/testing/e2eBridge.ts: keep both sides' additions (this
branch's MOCK_NCRYPTSEC/MOCK_BACKUP_PASSPHRASE fixtures and main's
personaSharePublicationCallCount counter)
Follow-up adjustments for main's refactor:
- egress_guard_tests.rs: retarget boundary 3 injection test from the
removed relay::submit_signed_event to submit_signed_event_at_with_keys;
update EVENTS_INVENTORY (relay.rs 3→2 sites, submit.rs shared funnel)
and add a test-fixture row for the mock relay route main added in
commands/personas/sharing.rs tests
- egress_guard.rs: update the boundary table for the moved funnel
- relay_admission.rs: update doc comment for the renamed entry point
Signed-off-by: Taylor Ho <taylorkmho@gmail.com >
2026-07-28 15:42:23 -07:00
Will Pfleger and GitHub
3ece4461df
feat(desktop): apply WebKit rendering workarounds at startup on Linux ( #3271 )
...
On some Linux GPU/driver/compositor combinations, WebKitGTK's dmabuf
renderer aborts the web process during startup, so Buzz comes up with no
window at all and the user has no way to fix it. Setting
`WEBKIT_DISABLE_DMABUF_RENDERER=1` avoids the abort by falling back to
the shared-memory buffer path.
WebKit reads each of its rendering variables exactly once per process,
so the choice has to be made before anything initializes — there is no
runtime toggle and no second chance later in the same process. This
decides up front from two cheap preflight signals rather than reacting
to a crash:
- **NVIDIA GPU** — any DRM device under `/sys/class/drm` reporting PCI
vendor `0x10de`, the driver family behind most upstream reports.
- **AppImage** — the `APPIMAGE` environment variable. linuxdeploy's
AppRun hook pins `GDK_BACKEND=x11`, and the dmabuf renderer buys nothing
on that XWayland path.
Either signal disables the dmabuf renderer. Neither signal leaves the
environment untouched.
## Escape hatches
`--safe-rendering` forces the safest configuration for one launch —
`WEBKIT_DISABLE_DMABUF_RENDERER` plus `WEBKIT_DISABLE_COMPOSITING_MODE`
— for a machine neither signal recognises.
Any user assignment of a variable this module may set stands the
heuristic down **wholesale**. Presence is the test, not truthiness, so
`VAR=0` and `VAR=` both count: a user asking for the dmabuf renderer
*on* gets it, even on a machine the heuristic would have opted out.
`--safe-rendering` against such an assignment is refused with a
diagnostic naming both the assignment and the key to unset, and exits
non-zero — the flag and the environment are two incompatible answers to
one question, and neither is guessed.
## Placement
`webkit_rendering::apply()` runs at the top of `fn main()`, before
`buzz_lib::run()`. That is the only point where the process is still
single threaded with no GTK object alive, which is what makes
`std::env::set_var` sound; the module doc and the call site both say so.
The whole module is `#[cfg(target_os = "linux")]` — macOS and Windows
compile none of it.
The decision is a pure function of argv, an injected environment lookup,
and an injected DRM root, so all of it is unit-testable without mutating
the process environment.
Closes #2338 . Upstream:
[tauri#9394](https://github.com/tauri-apps/tauri/issues/9394 ). Same
approach and same variable as
[clash-verge-rev](https://github.com/clash-verge-rev/clash-verge-rev/blob/main/src-tauri/src/utils/linux/workarounds.rs )
`workarounds.rs` and
[screenpipe](https://github.com/screenpipe/screenpipe/blob/main/apps/screenpipe-app-tauri/src-tauri/src/linux_webkit_env.rs )
`linux_webkit_env.rs`.
Signed-off-by: Will Pfleger <pfleger.will@gmail.com >
2026-07-28 17:20:29 -04:00
a35771fc44
feat(desktop): refine agent catalog sharing ( #2439 )
...
## Summary
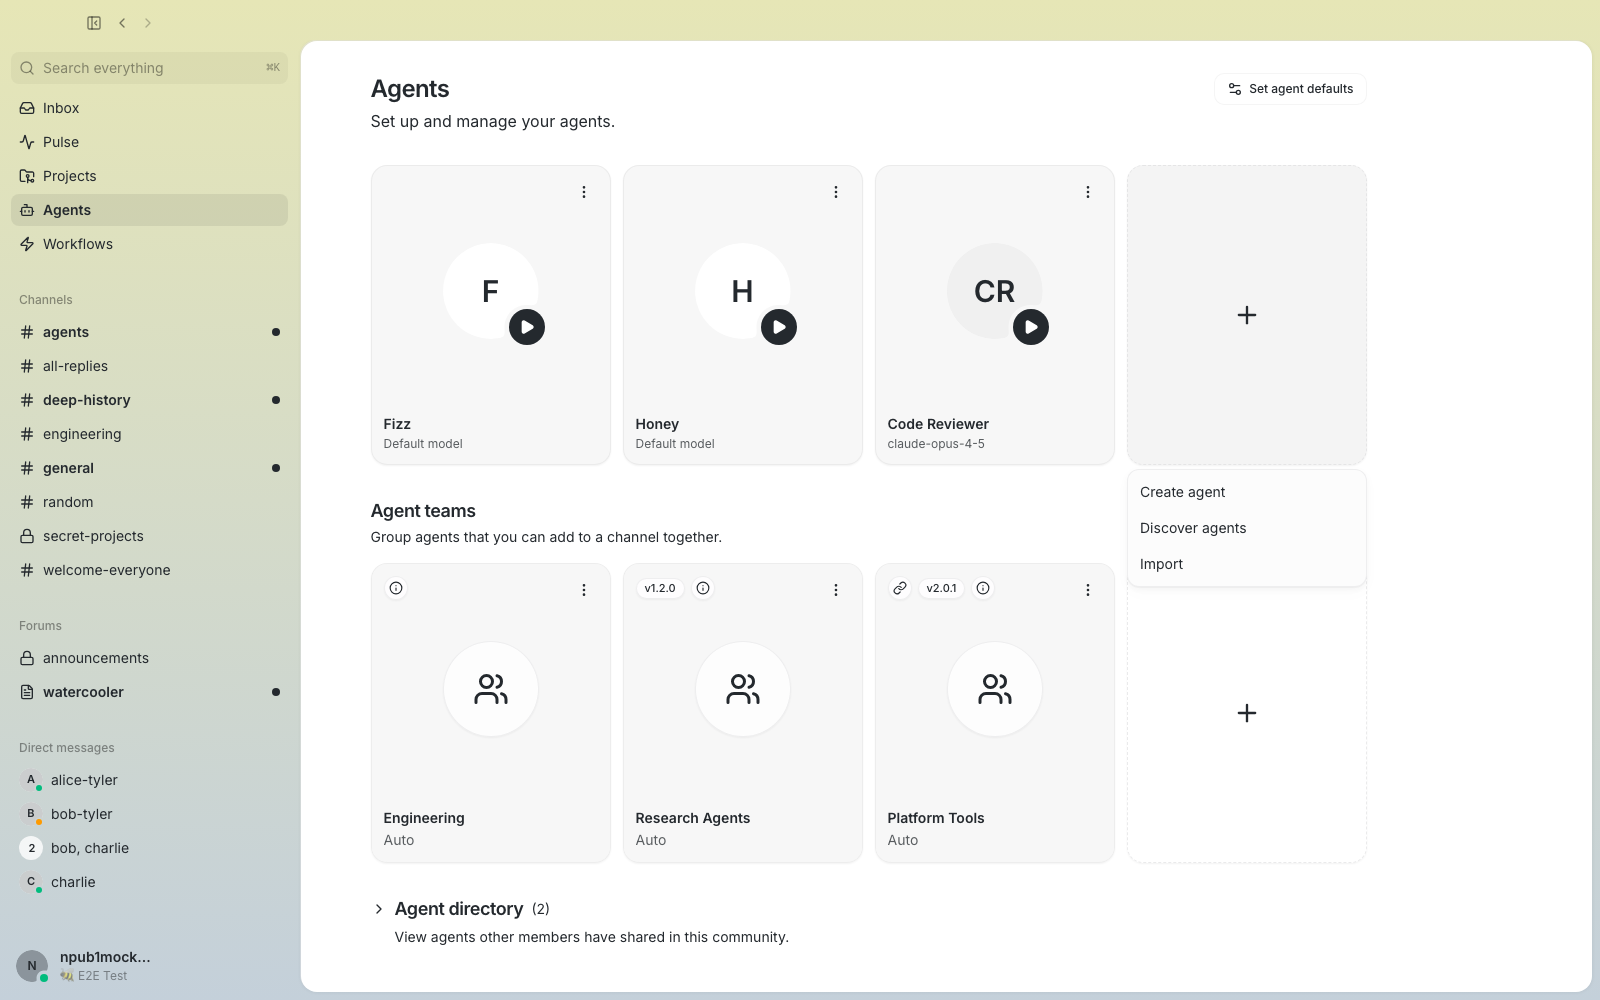
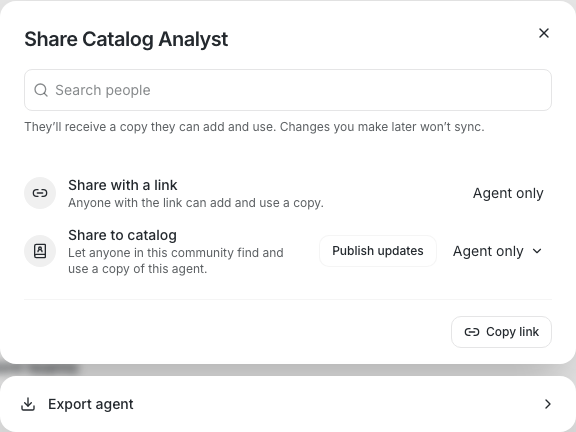
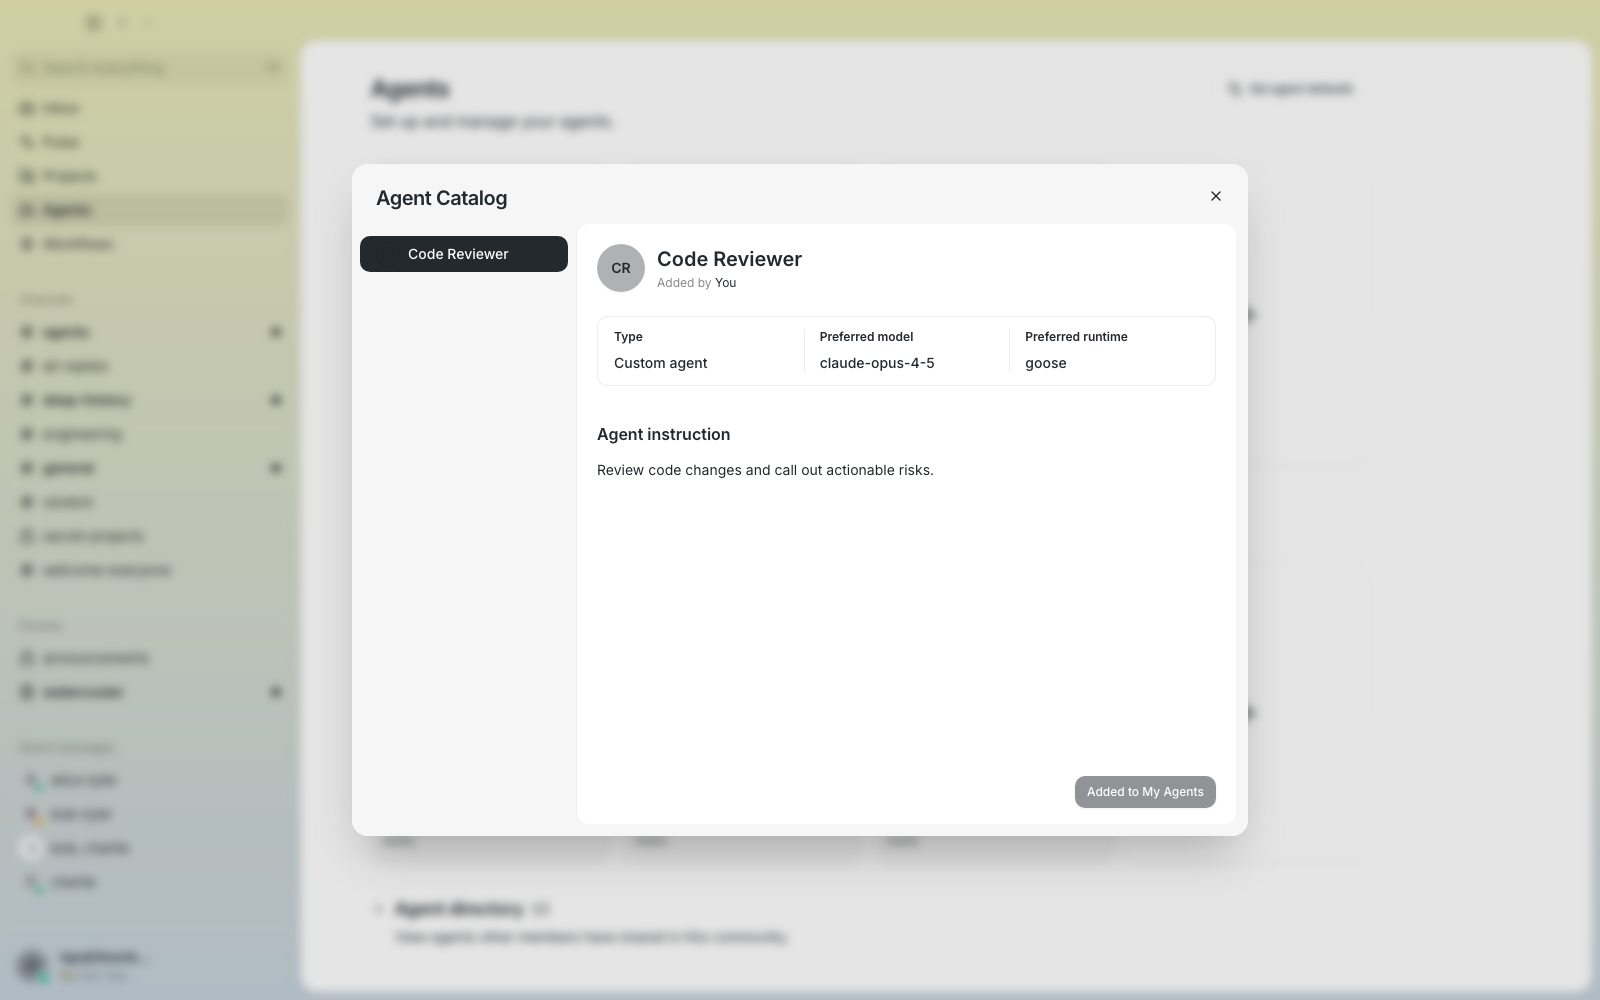
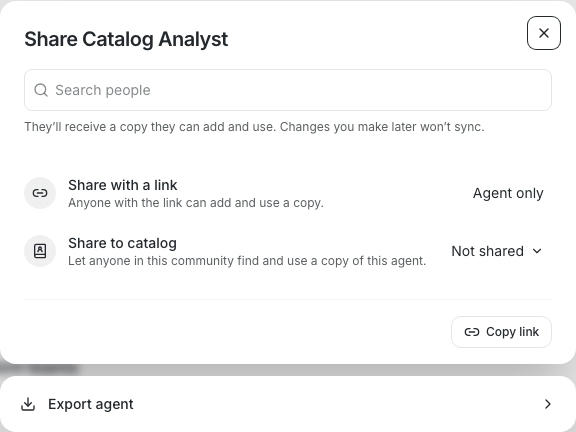
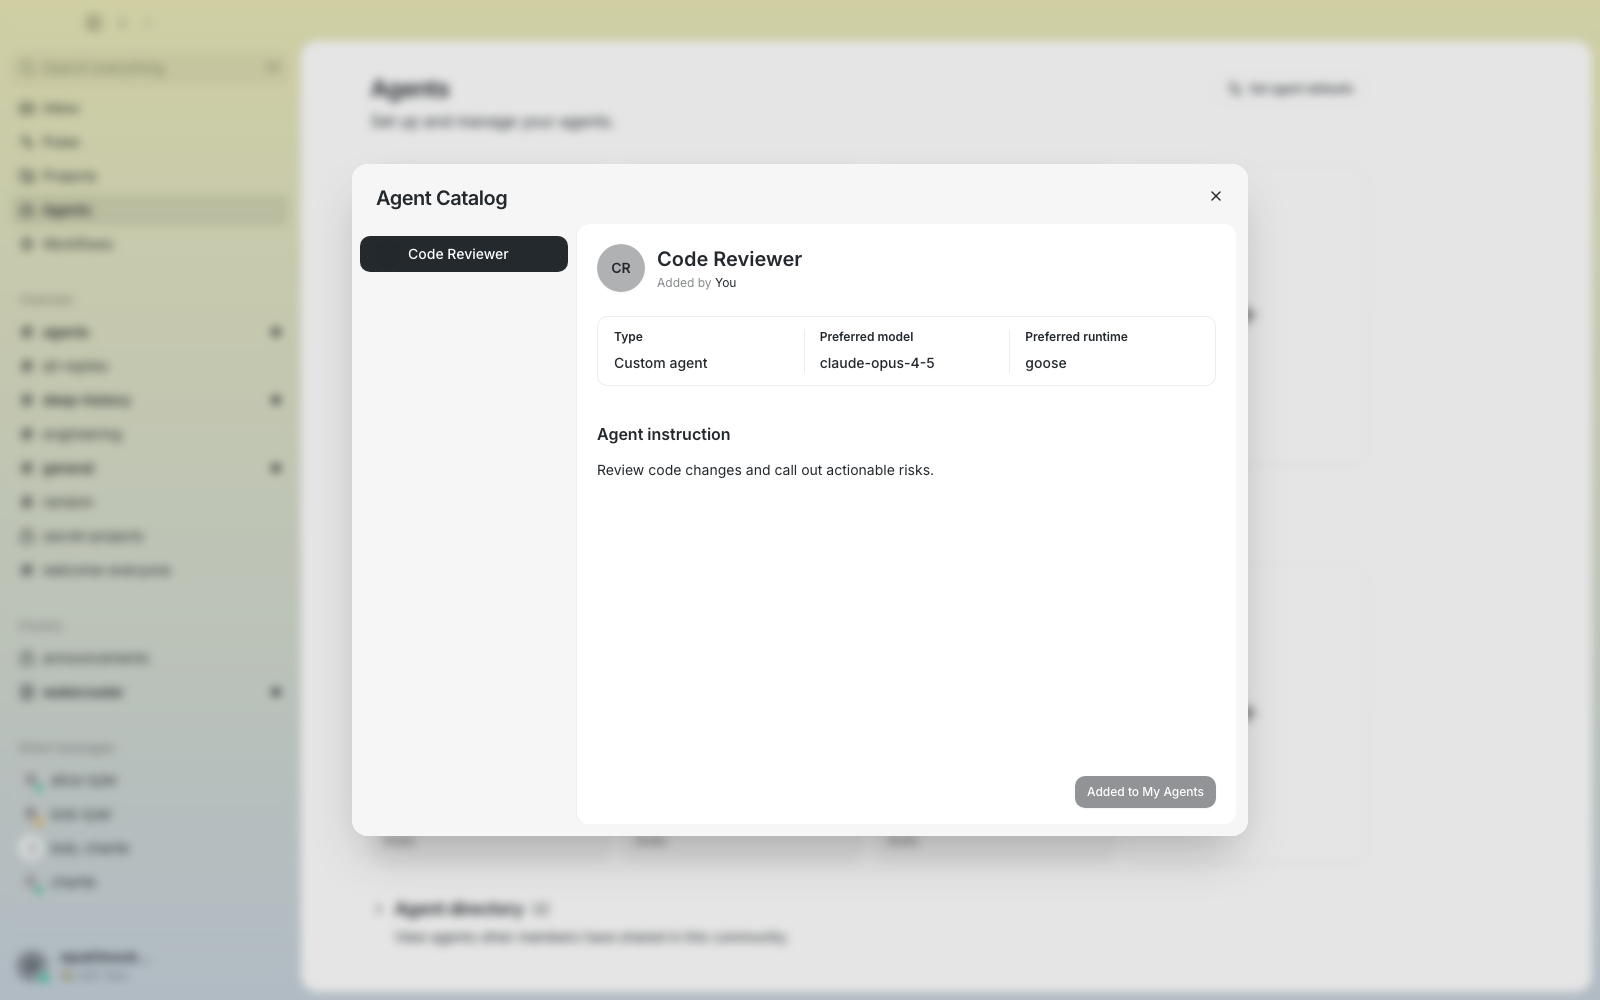
- add custom-agent catalog sharing and hide built-ins from discovery
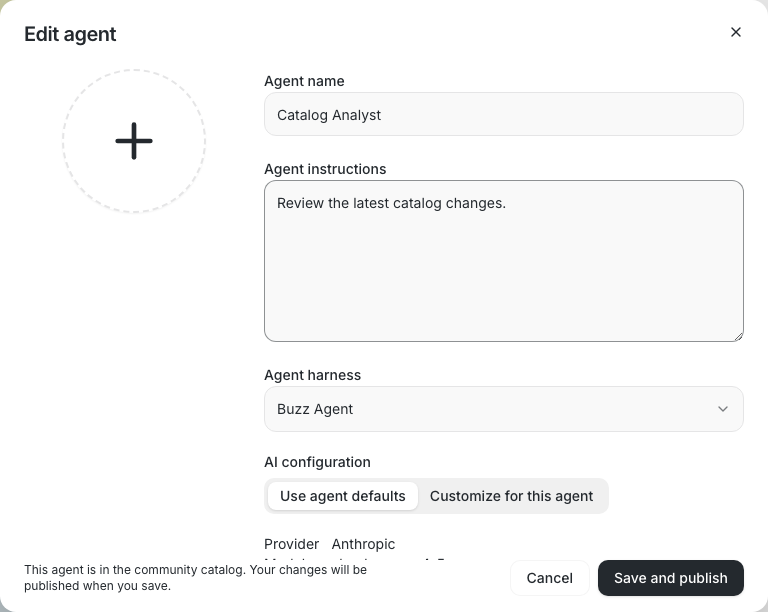
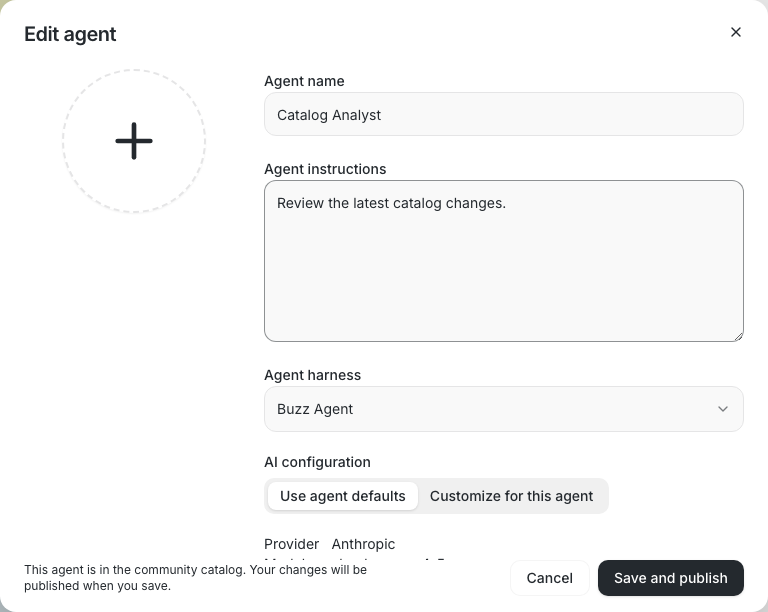
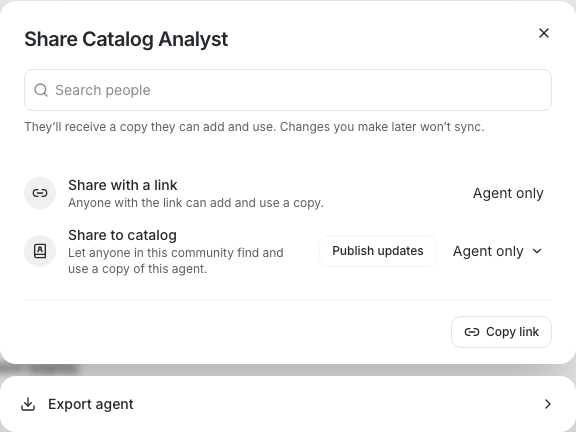
- let owners publish later catalog updates from Share or while saving
edits — the save always persists locally, and the publish reports
`published` or `queued` (flushed automatically once the relay is
reachable again)
- preserve agent type, model, and runtime across snapshot import/export
- simplify agent and team entry points and tighten catalog layout
- migrate the legacy global retention queue into the owner's active
scope so pending catalog publishes survive the upgrade
- keep the agent list and edits usable in recovery mode by degrading to
unshared projections when scope resolution or the retention DB fails
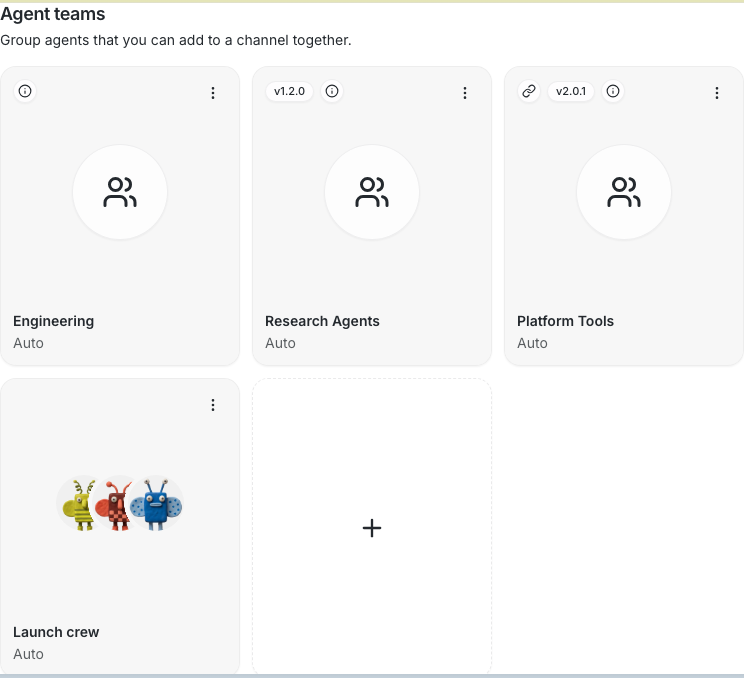
- track catalog provenance on copied personas, so adding an
already-added foreign agent resolves to the existing copy instead of
creating a duplicate
- scope inbound persona events to the community relay they arrived on
- page the catalog read past the relay's 1,000-row query clamp
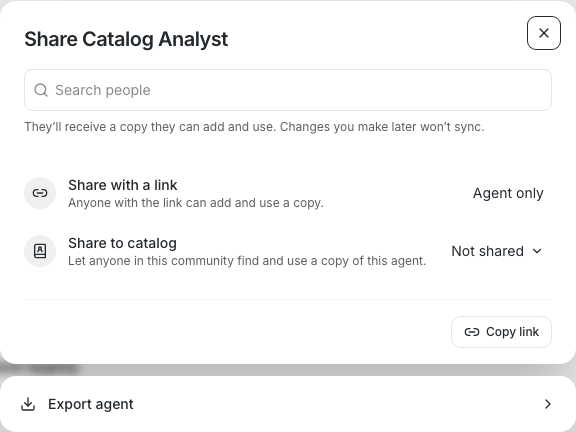
- unify the share dialog's memory-level choice into a single "What's
included" selector that drives both DM-send and copy-link delivery (all
six combinations preserved), group the delivery rows above the option
rows, and label the catalog toggle "Not shared" / "Shared"
- keep emoji avatars on catalog entries — they persist as inline
percent-encoded SVG, which the catalog projection's http(s)-only URL
guard used to drop, so a shared agent showed initials instead of its
avatar
- drop the "Active in communities" card from Agents settings, superseded
by the per-channel runtime controls in the members sidebar
## Screenshots
### Agent actions
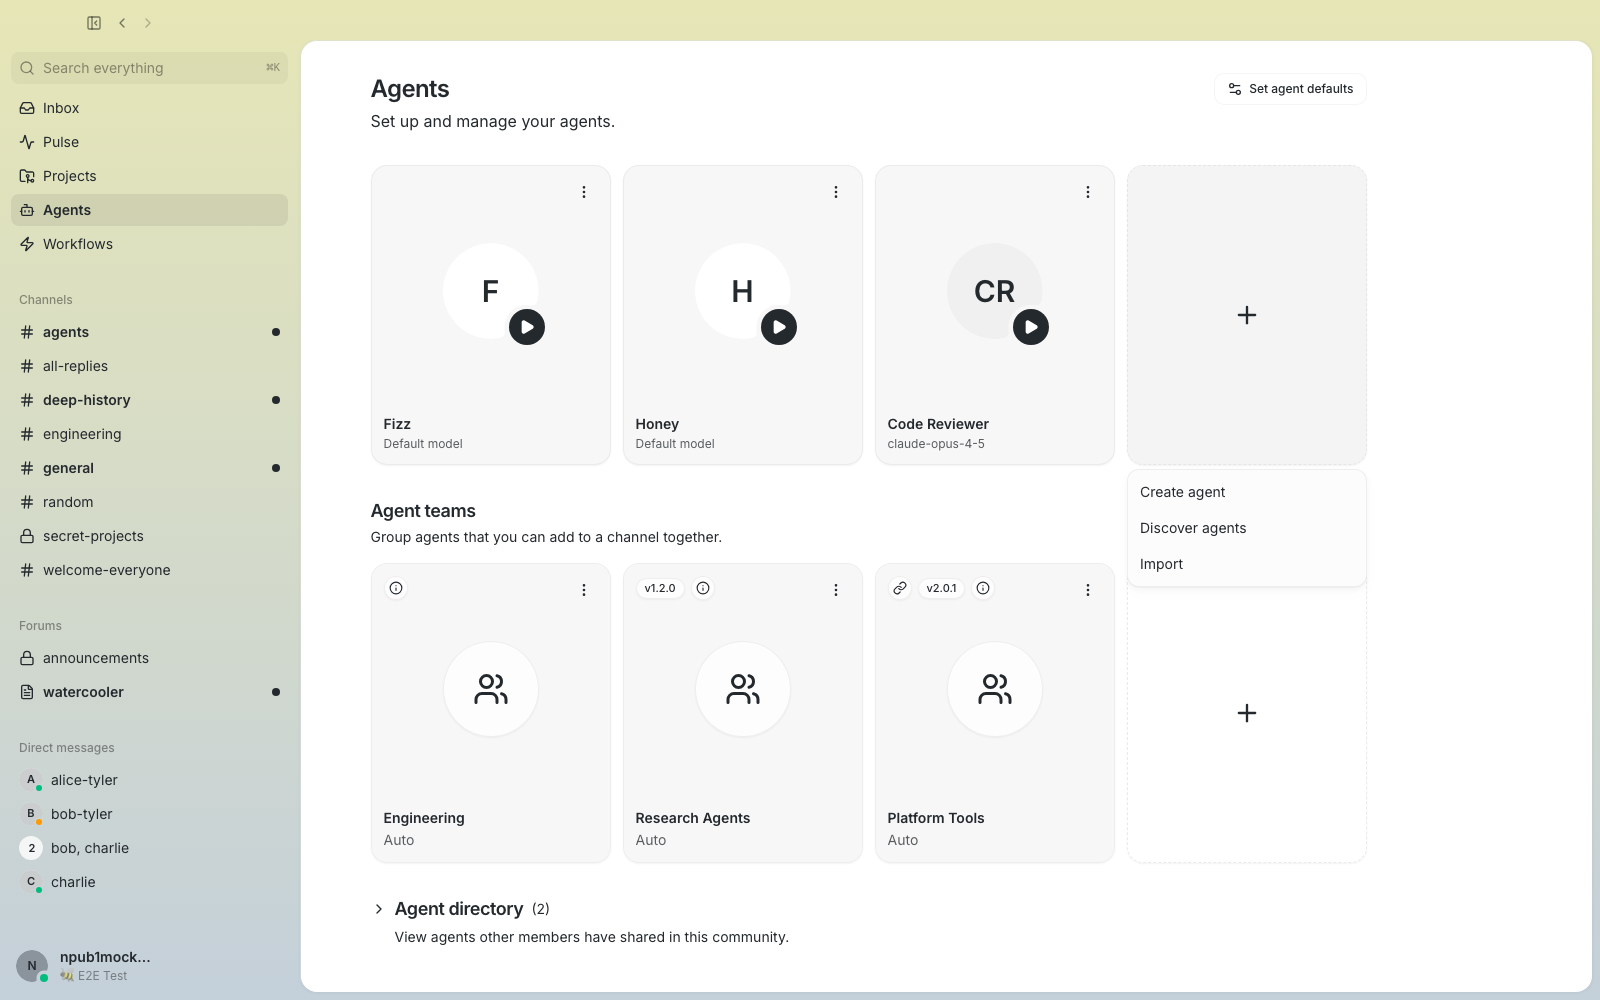
### Team avatar stack
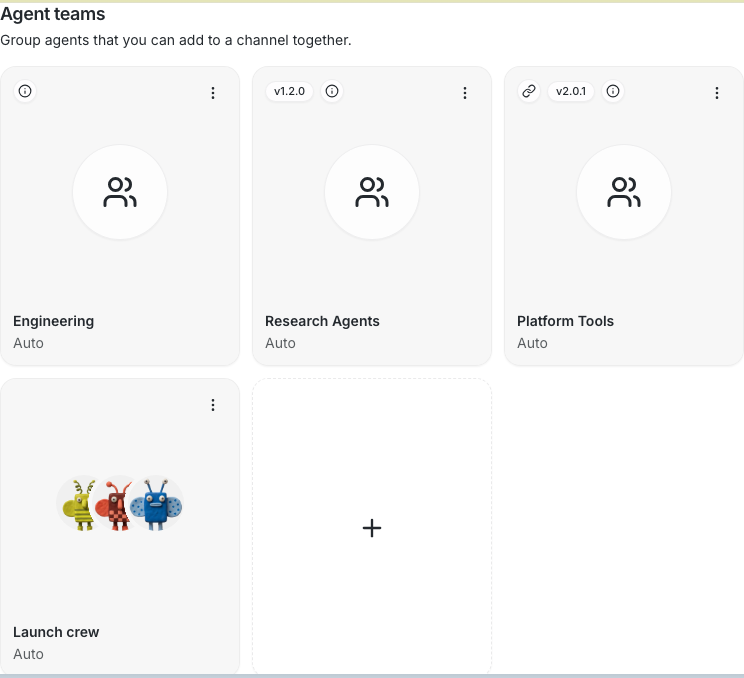
### Catalog sharing
### Publish while editing
### Publish from Share
### Catalog details
---------
Signed-off-by: kenny lopez <klopez4212@gmail.com >
Signed-off-by: Will Pfleger <pfleger.will@gmail.com >
Co-authored-by: Will Pfleger <pfleger.will@gmail.com >
2026-07-28 15:01:03 -04:00
npub1qyvc0c5kl4gqv2fd97fsk46tu378sqgy35vc83rvgfwne90sel7s0ed67d and Tyler Longwell
7a6a2cda51
Merge branch 'main' into eva/nip49-local-backup
...
* origin/main: (70 commits)
feat(relay): make Postgres pool size configurable, default 50 (#3191 )
Publish symbol-bearing debug relay images (#3250 )
feat(tracing): add datastore tracing plumbing (#2760 )
fix(buzz-acp): accept id-keyed config options when resolving model switch (#2795 )
fix(desktop): probe legacy Goose install dir on Windows (#3248 )
refactor(desktop): extract install command execution into install_exec (#3251 )
Polish composer activity layout and transitions (#3151 )
feat(invites): add use-limited invite links (#3141 )
fix(node): bump Buzz-supplied Node runtimes past OpenClaw's >=24.15.0 floor (#3218 )
fix(desktop): preserve thread anchor through layout reflow (#3212 )
feat(search): parse from:/in:/after:/before: and pass them in the filter (#2871 )
fix(desktop): fetch join policies through native networking (#2862 )
fix(desktop): republish agent identity records when a persona rename propagates (#2607 )
fix(desktop): keep project Inbox previews compact (#3193 )
Inbox refactor (#2045 )
Fix composer selection formatting and drop overlay (#3172 )
Refine pending message status (#3153 )
feat(admin): show reported message content in report detail (#3149 )
fix(desktop): recover full local storage on startup (#3182 )
Replace mobile reconnect banners with skeleton shimmer (#3143 )
...
Co-authored-by: Tyler Longwell <tlongwell@block.xyz >
Signed-off-by: Tyler Longwell <tlongwell@block.xyz >
2026-07-28 09:30:36 -04:00
John Matthew Tennant and GitHub
0019f80765
fix(desktop): fetch join policies through native networking ( #2862 )
...
## Context
Adding an existing community by relay URL could fail with `Community
rejected: Load failed` even when its WebSocket endpoint was reachable.
The Add Community flow fetched `/api/join-policy` from the WebView, so a
relay without a matching CORS allowance blocked the policy request
before the app could join it.
## Summary
This bug fix fetches join policies through Tauri's native networking
layer for direct URL joins. Invite-code discovery, policy acceptance,
and signed invite claims remain on the WebView path so those operations
can migrate together later.
## Changes
- Uses native networking for Add Community and first-community direct
URL join-policy requests.
- Validates relay schemes, rejects URLs containing credentials, and
refuses redirects.
- Bounds declared and chunked native responses before JSON parsing.
- Preserves existing `404`, non-success status, malformed JSON, and
absent-policy behavior.
- Requires every join-policy caller to choose its transport explicitly.
Public relays using Buzz's default permissive CORS configuration are not
known to be affected.
### Related issue
Related to #2872 .
### Testing
#### Reviewer-reproducible examples
End-to-end red/green requires a relay with restrictive CORS and a Buzz
identity authorized to join it.
##### Red: `main`
From a clean checkout of `main`:
```bash
. ./bin/activate-hermit
just staging
```
In Buzz Desktop:
1. Add another community so the restrictive-CORS relay can be removed.
2. Remove that relay.
3. Open Add Community and enter the relay's WebSocket URL.
4. Select Add Community.
Observed result:
```text
Community rejected: Load failed
```
##### Green: this PR
From a clean checkout of this branch:
```bash
. ./bin/activate-hermit
just staging
```
Repeat the same steps above.
Observed result:
```text
The community rejoins successfully.
```
Supporting checks:
- Six native join-policy tests, including oversized declared and chunked
responses.
- Four TypeScript API tests, including the native command contract.
- E2E build and four focused onboarding and sidebar Playwright tests.
- Full `just ci` and pre-push suites.
- Builderbot, Kalvin, and minimize-diff review fanout found no
actionable issues after the final rebase.
2026-07-27 17:52:36 -04:00
95fdf97880
feat(acp): bring your own harness (BYOH) — generic ACP runtime seam + settings gallery ( #2773 )
...
## What
Implements a "bring your own harness" (BYOH) generic ACP mechanism —
replacing per-harness backend code with a data-driven 3-tier system:
- **Tier 1 (compiled-in builtins):** goose, claude, codex, buzz-agent —
unchanged behavior
- **Tier 2 (bundled presets):** cursor, omp, grok, opencode, kimi, amp,
hermes, openclaw, and any future additions — defined in
`PRESET_HARNESSES`, no code duplication, icons stay
TerminalSquare/bundled-asset-only
- **Tier 3 (user-defined custom):** JSON definitions saved to
`custom_harnesses/` under app data; managed via Settings → Agents UI
## Changes
### Core data model
- `HarnessDefinition` — id, label, command, args, env, install URL/hint
- `PRESET_HARNESSES` static table — single source of truth for all
presets; `preset_harness_ids()` derives reserved IDs (D-11: no
hand-maintained copy)
- `source: "builtin" | "preset" | "custom"` tagging on every catalog
entry
### Persistence (B-4, B-6)
- `save_custom_harness_to_dir(dir, definition, rename_old_id)` —
backup-swap atomic write (backs up target → .bak, commits temp → target,
restores .bak on failure, removes .bak on success); safe on Windows
where `fs::rename` over an existing file is "access denied"
- `save_and_warm` / `delete_and_warm` — hold `PERSIST_MUTEX` for the
write + registry-warm pair, eliminating the lost-update race (B-6) where
two concurrent saves could interleave their warm calls and leave a stale
registry snapshot
- Validate-before-mutate: both IDs and env validated before any
filesystem mutation
### Env validation boundary (B-3)
- `validate_harness_definition_pub` calls `validate_user_env_keys` on
definition env at save AND load
- Rejects malformed keys (BUZZ_AUTH_TAG=x forgery shape), reserved keys
(BUZZ_MANAGED_AGENT etc.), NUL bytes, oversized values
### TypeScript boundary (B-2 / Thufir CRITICAL)
- `RawAcpRuntimeCatalogEntry` now declares `definition_env?:
Record<string,string>` and `source: "builtin" | "preset" | "custom"`
- `fromRawAcpRuntimeCatalogEntry` maps `definition_env → definitionEnv`
(camelCase); absent field defaults to `{}`
- Edit form reads `entry.definitionEnv` — env no longer erased on
save-then-edit cycle
### Unified descriptor (Phase A / Thufir F4)
- `EffectiveHarnessDescriptor { command, args, env }` in `readiness.rs`
- `resolve_effective_harness_descriptor()` — single resolver used by
spawn, spawn_hash, summary, get_agent_models (both saved and unsaved),
and readiness
- No competing arg-resolution forms
### Other fixes
- B-5: stop freezing `runtime.defaultArgs` into `record.agent_args` on
normal create paths
- B-7: readiness exec-check — `MissingBinary` variant for custom
commands not found on PATH
- B-8: onboarding transition — `setTimeout(0)` removed, parent-owned
route intent via `navigateAfterComplete` prop
- C-9: collector-discriminating sweep tests with injectable filters
- C-10: `HarnessManagementCard` uses `harnessGalleryLogic` helpers
(killed duplicate filter/sort)
- D-11: `BUILTIN_IDS` derived from `PRESET_HARNESSES` (no
hand-maintained copy)
- D-12: `mobile/pubspec.lock` churn reverted
- D-13: false ownership fast-path comment fixed
- D-14: URL scheme validation for `installInstructionsUrl`
- D-15: OpenClaw Gateway env-locus README line
### Tests added
**B-4 persistence (6 tests):**
`save_to_dir_create_writes_file_and_loads_back`,
`save_to_dir_same_id_edit_replaces_content`,
`save_to_dir_backup_is_cleaned_up_after_same_id_edit`,
`save_to_dir_rename_removes_old_file_and_creates_new`,
`save_to_dir_rename_nonexistent_old_id_is_non_fatal`,
`save_to_dir_roundtrip_with_env_preserves_values`
**B-3 env validation (6 tests):**
`validate_rejects_malformed_key_with_equals_sign`,
`validate_rejects_reserved_key_buzz_managed_agent`,
`validate_rejects_reserved_key_case_insensitive`,
`validate_rejects_nul_byte_in_value`,
`validate_rejects_value_over_per_value_size_limit`,
`validate_accepts_well_formed_env`
**B-2 API boundary (4 TS tests in tauri.test.mjs):**
`fromRawAcpRuntimeCatalogEntry maps definition_env to definitionEnv`,
`defaults definitionEnv to {} when absent`, `preserves source preset`,
`env round-trips through edit payload shape`
## Preset catalog
| ID | Label | Command |
|----|-------|---------|
| `cursor` | Cursor | `cursor-agent acp` |
| `omp` | Oh My Pi | `omp acp` |
| `grok` | Grok Build | `grok agent --always-approve stdio` |
| `opencode` | OpenCode | `opencode acp` |
| `kimi` | Kimi Code | `kimi acp` |
| `amp` | Amp | `amp-acp` |
| `hermes` | Hermes Agent | `hermes-acp` |
| `openclaw` | OpenClaw | `openclaw acp` |
## Review-fix pass (2026-07-26, Eva)
Fixes from the three-way review (Wren / Dawn / Eva) in the
buzz-generic-acp-harnesses thread, pushed as new commits (no rewrite):
1. **installHint edit round-trip** — form seeding extracted to
`formValuesFromCatalogEntry` (single source of truth), input rendered,
full-definition lossless round-trip regression.
2. **Dangling-delete coherence** — delete allowed; confirm counts
referencing agents (direct pin + persona-inherited); summary rows render
`harness (deleted): <id>`; spawn errors become actionable sentences
(`user_facing_harness_error`); composed delete→summary→start test.
3. **Comma-in-args** — rejected at `validate_harness_definition` (shared
by save AND disk load), mirrored inline in the form.
4. **Registry publish race** — collision/dup filtering moved into
`load_custom_harnesses` (both loaders inherit shadowing rules);
discovery publishes by re-reading the dir under `persist_mutex` (lock
scoped to publish only); deterministic interleaving regressions for
save-during-discovery and delete-during-discovery.
5. **Mechanical** — discarded `belongs_to_us` sweep arg deleted,
`load_global_agent_config` hoisted out of the per-record summary loop,
duplicated doc paragraph + stray SAFETY comment removed.
6. **PGID test de-flaked** — leader kept alive through the assertion.
Known follow-up (filed in review, not blocking): file-size split-outs
queued in `check-file-sizes.mjs` entries.
## Gate table — head `bf53f1d60`
| Gate | Result |
|------|--------|
| `cargo test --lib` (desktop/src-tauri) | **1701 passed**, 0 failed, 14
ignored |
| desktop JS suite (`pnpm test`) | **3605 passed**, 0 failed |
| `tsc --noEmit` | clean |
| `biome check` + file-size/px/pubkey checks | clean |
| `cargo clippy --lib -- -D warnings` | clean |
| `cargo fmt --check` | clean |
PR head: `bf53f1d60e3cbd07392e1287b83bb37ba90d0d33` — includes merge of
origin/main (`c2a4ee711`, conflicts in agent_models composed with
#2890 's live Databricks discovery)
---------
Signed-off-by: Will Pfleger <pfleger.will@gmail.com >
Signed-off-by: tlongwell-block <109685178+tlongwell-block@users.noreply.github.com >
Signed-off-by: Tyler Longwell <tlongwell@block.xyz >
Co-authored-by: npub1mn7jgtj4w2pd0g0zeuhxsa6jy6p0rewxz4kujt98my82ahfmp72sxjexk7 <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz >
Co-authored-by: tlongwell-block <109685178+tlongwell-block@users.noreply.github.com >
Co-authored-by: Dawn (sprout agent) <c6237ef84fa537c78dcee78efd2d4e59f728859c7f194da42ac51ededfa0be05@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: Tyler Longwell <tlongwell@block.xyz >
Co-authored-by: npub1qyvc0c5kl4gqv2fd97fsk46tu378sqgy35vc83rvgfwne90sel7s0ed67d <011987e296fd5006292d2f930b574be47c7801048d1983c46c425d3c95f0cffd@buzz.block.builderlab.xyz >
2026-07-26 20:06:20 -04:00
npub1qyvc0c5kl4gqv2fd97fsk46tu378sqgy35vc83rvgfwne90sel7s0ed67d and Tyler Longwell
e5cff3865d
Add NIP-49 encrypted local key backup: Rust layer + egress guard
...
Local-only ncryptsec backup of the identity key (plan:
PLANS/NIP49_LOCAL_BACKUP_PLAN.md Rev 3, approved 9/10 by Wren).
- key_backup.rs: NIP-49 codec (nostr nip49, log_n 18), one-artifact-per-
action create with decrypt-verify against the live pubkey, atomic 0o600
write + reread/byte-compare, EFF-wordlist passphrase generation,
ncryptsec import recovery, stale-backup cleanup on identity change.
- commands/identity.rs: create_ncryptsec_backup (whole body under
identity_mutation; webview can never supply canonical blob bytes),
save_ncryptsec_copy (dialog selection only + secret-file write, never
mutates app state), generate_backup_passphrase, import_identity now
accepts ncryptsec1 with a passphrase (raw-nsec path byte-for-byte
unchanged).
- egress_guard.rs: the backup must NEVER be transmitted to a relay —
fail-closed runtime guard rejecting ncryptsec1 at all 8 relay egress
boundaries (submit funnel, 3x relay.rs, huddle STT, both engram
submitters, native websocket send loop). Scope is ncryptsec1 only:
pairing intentionally carries the raw nsec inside its encrypted
NIP-AB session.
- Tests: injection test per boundary (8), /events inventory-completeness
tripwire, ncryptsec source-allowlist scan, spec vector, NFKC cross-form,
0600/atomicity/lifecycle, recovery-mode gating, concurrent identity
swap vs backup, boot-reset wipes the backup.
Co-authored-by: Tyler Longwell <tlongwell@block.xyz >
Signed-off-by: Tyler Longwell <tlongwell@block.xyz >
2026-07-25 22:44:03 -04:00
Will Pfleger and GitHub
bcca885ba9
docs: replace VPN-vendor references with generic wording ( #2805 )
...
## Summary

- Replace all references to a specific corporate VPN product name with
generic "VPN" / "corporate VPN" / "VPN tunnel" / "VPN CLI" language
across 15 files (21 lines)
- Comment-only and doc-only changes — zero functional impact
- Keeps the OSS repo free of vendor-specific assumptions

`rg -i warp` returns zero hits after this change (excluding
`node_modules`, lockfiles).
2026-07-24 22:11:54 -04:00
thomaspblock and GitHub
9081ab0ec9
feat(desktop): make pull request reviews actionable ( #2510 )
2026-07-24 11:34:25 -04:00
9cc9652c7d
fix(desktop): shared-compute usability — share toggle, usage indicator, model resync ( #2448 )
...
Signed-off-by: Tyler Longwell <tlongwell@block.xyz >
Co-authored-by: Michael Neale <michael.neale@gmail.com >
Co-authored-by: npub1qyvc0c5kl4gqv2fd97fsk46tu378sqgy35vc83rvgfwne90sel7s0ed67d <011987e296fd5006292d2f930b574be47c7801048d1983c46c425d3c95f0cffd@buzz.block.builderlab.xyz >
Co-authored-by: Tyler Longwell <tlongwell@block.xyz >
2026-07-23 23:21:01 -07:00
e67303f603
Gate default relay auto-connect behind release flag ( #2589 )
...
Signed-off-by: npub1cl47vfhsqpqy9pwndphpm36vcp7vvz5h2js4qpqm5yewzj7nutkq7xyw8c <c7ebe626f000404285d3686e1dc74cc07cc60a9754a150041ba132e14bd3e2ec@buzz.block.builderlab.xyz >
Co-authored-by: Bradley Axen <baxen@squareup.com >
Co-authored-by: npub1cl47vfhsqpqy9pwndphpm36vcp7vvz5h2js4qpqm5yewzj7nutkq7xyw8c <c7ebe626f000404285d3686e1dc74cc07cc60a9754a150041ba132e14bd3e2ec@buzz.block.builderlab.xyz >
2026-07-23 13:59:10 -07:00
80244f8231
Fix avatar upload lifecycle edge cases ( #2277 )
...
Signed-off-by: Logan Johnson <loganj@squareup.com >
Signed-off-by: npub1dpf98sl35hm9k65t8h6cvh5n6knn2msugh5k5nmysxwnw5wlh7uqn2wgp4 <685253c3f1a5f65b6a8b3df5865e93d5a7356e1c45e96a4f64819d3751dfbfb8@sprout-oss.stage.blox.sqprod.co >
Signed-off-by: npub13n66s06epmqf2kc3v373ez8hj65cuzyvxzjf93vwpervxqn2u7jq2qd9je <8cf5a83f590ec0955b11647d1c88f796a98e088c30a492c58e0e46c3026ae7a4@buzz.block.builderlab.xyz >
Co-authored-by: npub1dpf98sl35hm9k65t8h6cvh5n6knn2msugh5k5nmysxwnw5wlh7uqn2wgp4 <685253c3f1a5f65b6a8b3df5865e93d5a7356e1c45e96a4f64819d3751dfbfb8@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub13n66s06epmqf2kc3v373ez8hj65cuzyvxzjf93vwpervxqn2u7jq2qd9je <8cf5a83f590ec0955b11647d1c88f796a98e088c30a492c58e0e46c3026ae7a4@buzz.block.builderlab.xyz >
2026-07-23 12:45:00 -07:00
+2
61cc738ee8
feat(desktop+acp): spawn a harness per (agent, community) pair at GUI startup — warm sockets, lazy LLM pool ( #2122 )
...
Signed-off-by: Tyler Longwell <tlongwell@block.xyz >
Signed-off-by: Matt Toohey <contact@matttoohey.com >
Signed-off-by: npub12gtutshhh76rx0jx697f32f9tffd4hhp3hx58fp4x6u4uemkm7sqf8f757 <5217c5c2f7bfb4333e46d17c98a9255a52dadee18dcd43a43536b95e6776dfa0@sprout-oss.stage.blox.sqprod.co >
Signed-off-by: Tyler <109685178+tlongwell-block@users.noreply.github.com >
Co-authored-by: npub1jh9wn95s0472h86ahapupaf7m6kx4v9sx2n0atj2hltcfer8k06s5n3pyf <95cae996907d7cab9f5dbf43c0f53edeac6ab0b032a6feae4abfd784e467b3f5@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: Tyler Longwell <tlongwell@block.xyz >
Co-authored-by: npub12gtutshhh76rx0jx697f32f9tffd4hhp3hx58fp4x6u4uemkm7sqf8f757 <5217c5c2f7bfb4333e46d17c98a9255a52dadee18dcd43a43536b95e6776dfa0@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub1mprnacetjua2xx3p5eddmhxyk6wv929ymm5py8kd2xfxurxahspqqlgyta <d8473ee32b973aa31a21a65adddcc4b69cc2a8a4dee8121ecd51926e0cddbc02@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub1t2tgm7d8f995uqvmnm8h88sg3wnpp9a5xysjf6dg3tjmgt3ltulqdp8ehr <5a968df9a7494b4e019b9ecf739e088ba61097b4312124e9a88ae5b42e3f5f3e@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: Dawn <c6237ef84fa537c78dcee78efd2d4e59f728859c7f194da42ac51ededfa0be05@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub1qyvc0c5kl4gqv2fd97fsk46tu378sqgy35vc83rvgfwne90sel7s0ed67d <011987e296fd5006292d2f930b574be47c7801048d1983c46c425d3c95f0cffd@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: Matt Toohey <contact@matttoohey.com >
Co-authored-by: Claude Fable 5 <noreply@anthropic.com >
Co-authored-by: npub1hwqy0rnujtl25dzmlhn8qwux4kr8sjhas3ugltx9j5dm5dwkp2dsqjhytw <bb80478e7c92feaa345bfde6703b86ad86784afd84788facc5951bba35d60a9b@buzz.block.builderlab.xyz >
2026-07-22 13:24:46 -07:00
258cc92064
fix(desktop): survive degraded networks with rate-limit-aware relay client ( #2197 )
...
Signed-off-by: Will Pfleger <pfleger.will@gmail.com >
Co-authored-by: npub1mn7jgtj4w2pd0g0zeuhxsa6jy6p0rewxz4kujt98my82ahfmp72sxjexk7 <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub1fgdl5qqnh3k3f2xkqrvt7cujalhm623x4s7fdjdj5yrtp5fzjl9qrjpucw <4a1bfa0013bc6d14a8d600d8bf6392efefbd2a26ac3c96c9b2a106b0d12297ca@sprout-oss.stage.blox.sqprod.co >
2026-07-21 12:18:20 -04:00
thomaspblock and GitHub
b2c38c775b
feat(desktop): manage project branches ( #2212 )
2026-07-21 10:16:02 +02:00
fc1db46937
fix: skip membership lookup for open relays ( #2107 )
...
Signed-off-by: npub1ntr8jjcqq6gt06q5avvqttfjgpwshmra22pcmcagdnukw4ja4nqqsa9g54 <9ac6794b000690b7e814eb1805ad32405d0bec7d52838de3a86cf967565dacc0@sprout-oss.stage.blox.sqprod.co >
Signed-off-by: npub1dccv64krpcpse5cmkzfeh998cftungyatw3djt8jwdw6g43f7fyqzzmrf7 <6e30cd56c30e030cd31bb0939b94a7c257c9a09d5ba2d92cf2735da45629f248@sprout-oss.stage.blox.sqprod.co >
Signed-off-by: Tyler Longwell <tlongwell@block.xyz >
Co-authored-by: npub1ntr8jjcqq6gt06q5avvqttfjgpwshmra22pcmcagdnukw4ja4nqqsa9g54 <9ac6794b000690b7e814eb1805ad32405d0bec7d52838de3a86cf967565dacc0@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub1dccv64krpcpse5cmkzfeh998cftungyatw3djt8jwdw6g43f7fyqzzmrf7 <6e30cd56c30e030cd31bb0939b94a7c257c9a09d5ba2d92cf2735da45629f248@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: Eva <011987e296fd5006292d2f930b574be47c7801048d1983c46c425d3c95f0cffd@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: Tyler Longwell <tlongwell@block.xyz >
2026-07-20 15:35:40 +00:00
144b4f6c8d
fix(desktop): make invite QR downloadable ( #2168 )
...
Signed-off-by: npub12gtutshhh76rx0jx697f32f9tffd4hhp3hx58fp4x6u4uemkm7sqf8f757 <5217c5c2f7bfb4333e46d17c98a9255a52dadee18dcd43a43536b95e6776dfa0@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub12gtutshhh76rx0jx697f32f9tffd4hhp3hx58fp4x6u4uemkm7sqf8f757 <5217c5c2f7bfb4333e46d17c98a9255a52dadee18dcd43a43536b95e6776dfa0@sprout-oss.stage.blox.sqprod.co >
2026-07-20 15:29:22 +00:00
thomaspblock and GitHub
4fe3835e76
feat(desktop): add PR merge conflict recovery ( #2164 )
2026-07-20 13:41:33 +02:00
thomaspblock and GitHub
ed432f91d9
feat(desktop): complete project git workflows ( #2119 )
2026-07-19 22:09:56 +02:00
cd0e7402d7
Add owned community onboarding ( #2123 )
...
Signed-off-by: npub1rf6fvdj6ut0c4kcmjv4p5mmgh89nj58n69uu3fz3cvk3jn500hqs7emz79 <1a7496365ae2df8adb1b932a1a6f68b9cb3950f3d179c8a451c32d194e8f7dc1@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub1rf6fvdj6ut0c4kcmjv4p5mmgh89nj58n69uu3fz3cvk3jn500hqs7emz79 <1a7496365ae2df8adb1b932a1a6f68b9cb3950f3d179c8a451c32d194e8f7dc1@sprout-oss.stage.blox.sqprod.co >
2026-07-19 12:44:18 -07:00
8908bd6b71
Add native Builderlab auth and community client ( #2099 )
...
Signed-off-by: npub1rf6fvdj6ut0c4kcmjv4p5mmgh89nj58n69uu3fz3cvk3jn500hqs7emz79 <1a7496365ae2df8adb1b932a1a6f68b9cb3950f3d179c8a451c32d194e8f7dc1@sprout-oss.stage.blox.sqprod.co >
Signed-off-by: Bradley Axen <baxen@squareup.com >
Co-authored-by: npub1rf6fvdj6ut0c4kcmjv4p5mmgh89nj58n69uu3fz3cvk3jn500hqs7emz79 <1a7496365ae2df8adb1b932a1a6f68b9cb3950f3d179c8a451c32d194e8f7dc1@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: Claude Opus 4.8 (1M context) <noreply@anthropic.com >
2026-07-18 22:34:41 -07:00
4cf5694075
fix(desktop): own native WebSocket lifecycle ( #2076 )
...
Signed-off-by: npub1mprnacetjua2xx3p5eddmhxyk6wv929ymm5py8kd2xfxurxahspqqlgyta <d8473ee32b973aa31a21a65adddcc4b69cc2a8a4dee8121ecd51926e0cddbc02@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub1mprnacetjua2xx3p5eddmhxyk6wv929ymm5py8kd2xfxurxahspqqlgyta <d8473ee32b973aa31a21a65adddcc4b69cc2a8a4dee8121ecd51926e0cddbc02@sprout-oss.stage.blox.sqprod.co >
2026-07-18 18:52:56 +00:00
9f82850959
fix(desktop): route text copies through native clipboard ( #2054 )
...
Signed-off-by: npub1qvn3cujt28pg06ehlstrxyz6ayzp06t4uc7r566vxwwgrv24hglq9zju0n <03271c724b51c287eb37fc1633105ae90417e975e63c3a6b4c339c81b155ba3e@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub1qvn3cujt28pg06ehlstrxyz6ayzp06t4uc7r566vxwwgrv24hglq9zju0n <03271c724b51c287eb37fc1633105ae90417e975e63c3a6b4c339c81b155ba3e@sprout-oss.stage.blox.sqprod.co >
2026-07-18 00:01:24 +00:00
morgmart and GitHub
85fc64835e
Welcome new users with a live agent team kickoff ( #1998 )
...
Signed-off-by: morgmart <98432065+morgmart@users.noreply.github.com >
2026-07-17 07:39:03 -04:00
7b3513a34a
feat(desktop): allow agents to manage relay profiles ( #2009 )
...
Signed-off-by: npub12gtutshhh76rx0jx697f32f9tffd4hhp3hx58fp4x6u4uemkm7sqf8f757 <5217c5c2f7bfb4333e46d17c98a9255a52dadee18dcd43a43536b95e6776dfa0@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub12gtutshhh76rx0jx697f32f9tffd4hhp3hx58fp4x6u4uemkm7sqf8f757 <5217c5c2f7bfb4333e46d17c98a9255a52dadee18dcd43a43536b95e6776dfa0@sprout-oss.stage.blox.sqprod.co >
2026-07-16 20:47:32 -04:00
74f3f29758
feat(desktop): ensure starter channels during onboarding ( #1937 )
...
Signed-off-by: npub12gtutshhh76rx0jx697f32f9tffd4hhp3hx58fp4x6u4uemkm7sqf8f757 <5217c5c2f7bfb4333e46d17c98a9255a52dadee18dcd43a43536b95e6776dfa0@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub12gtutshhh76rx0jx697f32f9tffd4hhp3hx58fp4x6u4uemkm7sqf8f757 <5217c5c2f7bfb4333e46d17c98a9255a52dadee18dcd43a43536b95e6776dfa0@sprout-oss.stage.blox.sqprod.co >
2026-07-16 15:40:48 -04:00
8d3666c5f8
Guide CLI installation and subscription sign-in ( #1980 )
...
Signed-off-by: npub12gtutshhh76rx0jx697f32f9tffd4hhp3hx58fp4x6u4uemkm7sqf8f757 <5217c5c2f7bfb4333e46d17c98a9255a52dadee18dcd43a43536b95e6776dfa0@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub12gtutshhh76rx0jx697f32f9tffd4hhp3hx58fp4x6u4uemkm7sqf8f757 <5217c5c2f7bfb4333e46d17c98a9255a52dadee18dcd43a43536b95e6776dfa0@sprout-oss.stage.blox.sqprod.co >
2026-07-16 14:21:03 -04:00
a1626f96ce
fix(desktop): preserve relaunch through mesh shutdown ( #1966 )
...
Signed-off-by: Wes <wesbillman@users.noreply.github.com >
Co-authored-by: Pinky <44b8e82baa6e0e254e0208d68f335c283c94e7b78dd1fa10d5a49d3f13dd0435@sprout-oss.stage.blox.sqprod.co >
2026-07-16 10:57:13 -07:00
thomaspblock and GitHub
72a5c388d7
feat(desktop): Projects v3 — overview redesign, activity feed, agent access & sync controls ( #1851 )
2026-07-16 09:14:08 +02:00
8688c0416d
Rework first-launch community onboarding ( #1936 )
...
Signed-off-by: Wes <wesbillman@users.noreply.github.com >
Co-authored-by: Pinky <44b8e82baa6e0e254e0208d68f335c283c94e7b78dd1fa10d5a49d3f13dd0435@sprout-oss.stage.blox.sqprod.co >
2026-07-15 22:01:51 -07:00
e1865cb7f7
fix(desktop): stop marking users away while active on the machine ( #1942 )
...
Signed-off-by: Wes <wesbillman@users.noreply.github.com >
Co-authored-by: Brain <21994759fc7a6fa6b965551d35cfd7897d262f2495467f2d78694ddcfa6a5c7e@sprout-oss.stage.blox.sqprod.co >
2026-07-15 21:47:15 -07:00
klopez4212 and GitHub
2f3fa586f3
Polish agent and team sharing and snapshots ( #1852 )
2026-07-15 17:19:03 +00:00
f5c33d3335
feat(desktop): Send feedback modal + profile presence chip ( #1756 )
...
Signed-off-by: npub13fn4ahfnvaa2qwylvegdgeajqs0mph6v4qsw4jcqnw4mjh3hzh2quuucm5 <8a675edd33677aa0389f6650d467b2041fb0df4ca820eacb009babb95e3715d4@sprout-oss.stage.blox.sqprod.co >
Signed-off-by: Wes <wesbillman@users.noreply.github.com >
Co-authored-by: npub13fn4ahfnvaa2qwylvegdgeajqs0mph6v4qsw4jcqnw4mjh3hzh2quuucm5 <8a675edd33677aa0389f6650d467b2041fb0df4ca820eacb009babb95e3715d4@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: Wes <wesbillman@users.noreply.github.com >
Co-authored-by: Pinky <44b8e82baa6e0e254e0208d68f335c283c94e7b78dd1fa10d5a49d3f13dd0435@sprout-oss.stage.blox.sqprod.co >
2026-07-15 07:57:18 -07:00
Michael Neale and GitHub
54638ff4bb
mesh: upgrade runtime, enforce membership, add shared compute provider ( #1656 )
2026-07-15 10:10:29 -04:00
Will Pfleger and GitHub
4c106d8785
chore(desktop): replace setup ? operators with clean exit ( #1882 )
2026-07-14 19:48:05 -04:00
448baeef77
feat(teams): unify team model, snapshot sharing, and PNG memory parity ( #1846 )
...
Signed-off-by: Will Pfleger <pfleger.will@gmail.com >
Co-authored-by: npub1mn7jgtj4w2pd0g0zeuhxsa6jy6p0rewxz4kujt98my82ahfmp72sxjexk7 <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@sprout-oss.stage.blox.sqprod.co >
2026-07-14 17:10:51 -04:00
ccb021d713
Relay mesh: cross-pod tunnel + huddle transport (buzz-relay-mesh) ( #1670 )
...
Signed-off-by: Tyler Longwell <tlongwell@block.xyz >
Signed-off-by: npub1mprnacetjua2xx3p5eddmhxyk6wv929ymm5py8kd2xfxurxahspqqlgyta <d8473ee32b973aa31a21a65adddcc4b69cc2a8a4dee8121ecd51926e0cddbc02@sprout-oss.stage.blox.sqprod.co >
Signed-off-by: npub17jjz49l9jjmhhk7cac63j8yt9z555n9cw8vk7v5jz4vzw4ppld5qgj57cc <f4a42a97e594b77bdbd8ee35191c8b28a94a4cb871d96f32921558275421fb68@sprout-oss.stage.blox.sqprod.co >
Signed-off-by: Tyler Longwell <tlongwell@squareup.com >
Signed-off-by: tlongwell-block <109685178+tlongwell-block@users.noreply.github.com >
Co-authored-by: npub1qyvc0c5kl4gqv2fd97fsk46tu378sqgy35vc83rvgfwne90sel7s0ed67d <011987e296fd5006292d2f930b574be47c7801048d1983c46c425d3c95f0cffd@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: Tyler Longwell <tlongwell@block.xyz >
Co-authored-by: npub1mprnacetjua2xx3p5eddmhxyk6wv929ymm5py8kd2xfxurxahspqqlgyta <d8473ee32b973aa31a21a65adddcc4b69cc2a8a4dee8121ecd51926e0cddbc02@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub1cc3ha7z055mu0rwwu7806t2wt8mj3pvu0uv5mfp2c50dahaqhczshdalg6 <c6237ef84fa537c78dcee78efd2d4e59f728859c7f194da42ac51ededfa0be05@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub17jjz49l9jjmhhk7cac63j8yt9z555n9cw8vk7v5jz4vzw4ppld5qgj57cc <f4a42a97e594b77bdbd8ee35191c8b28a94a4cb871d96f32921558275421fb68@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub1jh9wn95s0472h86ahapupaf7m6kx4v9sx2n0atj2hltcfer8k06s5n3pyf <95cae996907d7cab9f5dbf43c0f53edeac6ab0b032a6feae4abfd784e467b3f5@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub1t2tgm7d8f995uqvmnm8h88sg3wnpp9a5xysjf6dg3tjmgt3ltulqdp8ehr <5a968df9a7494b4e019b9ecf739e088ba61097b4312124e9a88ae5b42e3f5f3e@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub12gtutshhh76rx0jx697f32f9tffd4hhp3hx58fp4x6u4uemkm7sqf8f757 <5217c5c2f7bfb4333e46d17c98a9255a52dadee18dcd43a43536b95e6776dfa0@sprout-oss.stage.blox.sqprod.co >
2026-07-14 16:56:48 -04:00
cf97237965
feat(desktop): add Sign Out to Settings to reset and relaunch ( #1842 )
...
Signed-off-by: Will Pfleger <pfleger.will@gmail.com >
Co-authored-by: npub1mn7jgtj4w2pd0g0zeuhxsa6jy6p0rewxz4kujt98my82ahfmp72sxjexk7 <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@sprout-oss.stage.blox.sqprod.co >
2026-07-14 16:52:57 -04:00
Noah and GitHub
3370cd0836
fix(desktop): stabilize agent identity restore ( #1831 )
2026-07-14 07:39:49 -07:00
020ac7f405
fix(desktop): resolve Git Bash for Windows shell tool via PATH/git/registry fallback ( #1821 )
...
Signed-off-by: Will Pfleger <pfleger.will@gmail.com >
Co-authored-by: npub1mn7jgtj4w2pd0g0zeuhxsa6jy6p0rewxz4kujt98my82ahfmp72sxjexk7 <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@sprout-oss.stage.blox.sqprod.co >
2026-07-13 16:53:02 -04:00
bea507d8aa
chore(ci): lint desktop Tauri crate in CI ( #1801 )
...
Signed-off-by: Will Pfleger <pfleger.will@gmail.com >
Co-authored-by: npub1mn7jgtj4w2pd0g0zeuhxsa6jy6p0rewxz4kujt98my82ahfmp72sxjexk7 <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@sprout-oss.stage.blox.sqprod.co >
2026-07-13 11:21:10 -04:00
150514f665
feat(desktop): add team snapshot sharing commands ( #1790 )
...
Signed-off-by: Will Pfleger <pfleger.will@gmail.com >
Co-authored-by: npub1mn7jgtj4w2pd0g0zeuhxsa6jy6p0rewxz4kujt98my82ahfmp72sxjexk7 <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@sprout-oss.stage.blox.sqprod.co >
2026-07-13 00:43:06 -04:00
1fa91f5691
refactor(desktop): remove legacy persona-card flows ( #1781 )
...
Signed-off-by: Will Pfleger <pfleger.will@gmail.com >
Co-authored-by: npub1mn7jgtj4w2pd0g0zeuhxsa6jy6p0rewxz4kujt98my82ahfmp72sxjexk7 <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@sprout-oss.stage.blox.sqprod.co >
2026-07-12 21:05:03 -04:00
1580046b3c
feat(desktop): add buzz-agent-snapshot v1 export, import, sender-native send, and recipient card/import ( #1753 )
...
Signed-off-by: Will Pfleger <pfleger.will@gmail.com >
Co-authored-by: npub1mn7jgtj4w2pd0g0zeuhxsa6jy6p0rewxz4kujt98my82ahfmp72sxjexk7 <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@sprout-oss.stage.blox.sqprod.co >
2026-07-12 19:30:21 -04:00
89e2e2e4ad
Fix desktop launch motion and reaction spacing ( #1717 )
...
Co-authored-by: Fizz <8a675edd33677aa0389f6650d467b2041fb0df4ca820eacb009babb95e3715d4@sprout-oss.stage.blox.sqprod.co >
2026-07-12 08:42:31 -07:00
77c08365e4
feat(desktop): global agent config defaults with readiness/spawn parity ( #1448 )
...
Signed-off-by: Will Pfleger <pfleger.will@gmail.com >
Co-authored-by: npub1mn7jgtj4w2pd0g0zeuhxsa6jy6p0rewxz4kujt98my82ahfmp72sxjexk7 <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@sprout-oss.stage.blox.sqprod.co >
2026-07-10 13:38:33 -04:00
e15f068571
fix(desktop): stop losing imported identity on every launch ( #1568 )
...
Signed-off-by: Will Pfleger <pfleger.will@gmail.com >
Co-authored-by: npub1mn7jgtj4w2pd0g0zeuhxsa6jy6p0rewxz4kujt98my82ahfmp72sxjexk7 <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@sprout-oss.stage.blox.sqprod.co >
2026-07-09 17:58:36 -04:00
6b2147a5d1
fix(desktop): honor macOS title-bar double-click preference ( #1674 )
...
Signed-off-by: npub13fn4ahfnvaa2qwylvegdgeajqs0mph6v4qsw4jcqnw4mjh3hzh2quuucm5 <8a675edd33677aa0389f6650d467b2041fb0df4ca820eacb009babb95e3715d4@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub13fn4ahfnvaa2qwylvegdgeajqs0mph6v4qsw4jcqnw4mjh3hzh2quuucm5 <8a675edd33677aa0389f6650d467b2041fb0df4ca820eacb009babb95e3715d4@sprout-oss.stage.blox.sqprod.co >
2026-07-09 17:27:08 +01:00
thomaspblock and GitHub
58fe9388c8
feat(desktop): projects overview v2 — aggregate rail, PR review flow, commit detail, and straighter layout ( #1677 )
2026-07-09 18:24:19 +02:00
cdba2a08e1
Polish Buzz sidebar theme ( #1671 )
...
Signed-off-by: npub13fn4ahfnvaa2qwylvegdgeajqs0mph6v4qsw4jcqnw4mjh3hzh2quuucm5 <8a675edd33677aa0389f6650d467b2041fb0df4ca820eacb009babb95e3715d4@sprout-oss.stage.blox.sqprod.co >
Co-authored-by: npub13fn4ahfnvaa2qwylvegdgeajqs0mph6v4qsw4jcqnw4mjh3hzh2quuucm5 <8a675edd33677aa0389f6650d467b2041fb0df4ca820eacb009babb95e3715d4@sprout-oss.stage.blox.sqprod.co >
2026-07-09 08:10:24 -07:00